Vulnerability database
Every flaw the U.S. government’s cybersecurity agency (CISA) has confirmed attackers are using, plus the new WordPress plugin and theme bugs published each day, sorted by what they mean for a small business. We refresh it twice a day. If you see something your website or office runs, tell us.
16 results
Sep 3, 2026Label Studio fails to apply organization filters when resolving storage URIs for tasks and projects in proxy_api.py endpoints.CVE-2026-85211 · Other software · HumanSignal · reported by VulnCheckHigh 8.3
Label Studio fails to apply organization filters when resolving storage URIs for tasks and projects in proxy_api.py endpoints. Attackers can access other tenants' cloud storage objects by creating a separate organization and supplying arbitrary file URIs to presign or stream bucket contents.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Sep 3, 2026Label Studio through 1.23.0 fails to validate webhook URLs, allowing authenticated users to dispatch requests to internal services including RFC 1918 addresses CVE-2026-85179 · Other software · HumanSignal · reported by VulnCheckHigh 8.4
Label Studio through 1.23.0 fails to validate webhook URLs, allowing authenticated users to dispatch requests to internal services including RFC 1918 addresses and cloud metadata endpoints. Attackers can create webhooks targeting private networks and exfiltrate annotation data by enabling payload transmission in outbound requests.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Aug 24, 2026Label Studio does not scope the annotation detail endpoint to the requesting user's organization.CVE-2026-76073 · Other software · HumanSignal · reported by VulnCheckHigh 8.7
Label Studio does not scope the annotation detail endpoint to the requesting user's organization. AnnotationAPI in label_studio/tasks/api.py declares queryset = Annotation.objects.all() and provides no get_queryset override, so the default lookup retrieves any annotation by primary key. The view's permission_required entries name annotations.view, annotations.change and annotations.delete, and label_studio/core/permissions.py registers every permission with rules.is_authenticated, so the check is satisfied by any logged-in account and no object-level organization test runs. The sibling task endpoint does constrain its queryset with project__organization set to the requester's active organization, which is the boundary this path omits. Annotation identifiers are sequential integers, so an authenticated user of one organization can enumerate identifiers to read, modify and delete annotations belonging to other organizations on the same instance. The same unscoped queryset appears on AnnotationConvertAPI in the same file.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Aug 11, 2026A server-side request forgery vulnerability in HumanSignal Label Studio through 1.24.0.dev0 exists because SSRF_PROTECTION_ENABLED is set to false by default.CVE-2026-72560 · Other software · HumanSignal · reported by 309f9ea4-e3e9-4c6c-b79d-e8eb01244f2cMedium 6.5
A server-side request forgery vulnerability in HumanSignal Label Studio through 1.24.0.dev0 exists because SSRF_PROTECTION_ENABLED is set to false by default. The import-from-URL endpoint fetches any caller-supplied URL including internal loopback addresses on the default installation. An authenticated user can use this to reach internal services, cloud metadata endpoints, and other resources not intended for external access.
- Product
- Label Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 12, 2026Label Studio is a multi-type data labeling and annotation tool.CVE-2026-22033 · Other software · HumanSignal · reported by GitHubHigh 8.6
Label Studio is a multi-type data labeling and annotation tool. In 1.22.0 and earlier, a persistent stored cross-site scripting (XSS) vulnerability exists in the custom_hotkeys functionality of the application. An authenticated attacker (or one who can trick a user/administrator into updating their custom_hotkeys) can inject JavaScript code that executes in other users’ browsers when those users load any page using the templates/base.html template. Because the application exposes an API token endpoint (/api/current-user/token) to the browser and lacks robust CSRF protection on some API endpoints, the injected script may fetch the victim’s API token or call token reset endpoints — enabling full account takeover and unauthorized API access.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
May 14, 2025Label Studio is a multi-type data labeling and annotation tool.CVE-2025-47783 · Other software · HumanSignal · reported by GitHubHigh 7.6
Label Studio is a multi-type data labeling and annotation tool. A vulnerability in versions prior to 1.18.0 allows an attacker to inject a malicious script into the context of a web page, which can lead to data theft, session hijacking, unauthorized actions on behalf of the user, and other attacks. The vulnerability is reproducible when sending a properly formatted request to the `POST /projects/upload-example/` endpoint. In the source code, the vulnerability is located at `label_studio/projects/views.py`. Version 1.18.0 contains a patch for the issue.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 14, 2025Label Studio is an open source data labeling tool.CVE-2025-25297 · Other software · HumanSignal · reported by GitHubHigh 8.6
Label Studio is an open source data labeling tool. Prior to version 1.16.0, Label Studio's S3 storage integration feature contains a Server-Side Request Forgery (SSRF) vulnerability in its endpoint configuration. When creating an S3 storage connection, the application allows users to specify a custom S3 endpoint URL via the s3_endpoint parameter. This endpoint URL is passed directly to the boto3 AWS SDK without proper validation or restrictions on the protocol or destination. The vulnerability allows an attacker to make the application send HTTP requests to arbitrary internal services by specifying them as the S3 endpoint. When the storage sync operation is triggered, the application attempts to make S3 API calls to the specified endpoint, effectively making HTTP requests to the target service and returning the response in error messages. This SSRF vulnerability enables attackers to bypass network segmentation and access internal services that should not be accessible from the external network. The vulnerability is particularly severe because error messages from failed requests contain the full response body, allowing data exfiltration from internal services. Version 1.16.0 contain
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 14, 2025Label Studio is an open source data labeling tool.CVE-2025-25296 · Other software · HumanSignal · reported by GitHubMedium 6.1
Label Studio is an open source data labeling tool. Prior to version 1.16.0, Label Studio's `/projects/upload-example` endpoint allows injection of arbitrary HTML through a `GET` request with an appropriately crafted `label_config` query parameter. By crafting a specially formatted XML label config with inline task data containing malicious HTML/JavaScript, an attacker can achieve Cross-Site Scripting (XSS). While the application has a Content Security Policy (CSP), it is only set in report-only mode, making it ineffective at preventing script execution. The vulnerability exists because the upload-example endpoint renders user-provided HTML content without proper sanitization on a GET request. This allows attackers to inject and execute arbitrary JavaScript in victims' browsers by getting them to visit a maliciously crafted URL. This is considered vulnerable because it enables attackers to execute JavaScript in victims' contexts, potentially allowing theft of sensitive data, session hijacking, or other malicious actions. Version 1.16.0 contains a patch for the issue.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 14, 2025Label Studio is an open source data labeling tool.CVE-2025-25295 · Other software · HumanSignal · reported by GitHubHigh 8.7
Label Studio is an open source data labeling tool. A path traversal vulnerability in Label Studio SDK versions prior to 1.0.10 allows unauthorized file access outside the intended directory structure. The flaw exists in the VOC, COCO and YOLO export functionalities. These functions invoke a `download` function on the `label-studio-sdk` python package, which fails to validate file paths when processing image references during task exports. By creating tasks with path traversal sequences in the image field, an attacker can force the application to read files from arbitrary server filesystem locations when exporting projects in any of the mentioned formats. This is authentication-required vulnerability allowing arbitrary file reads from the server filesystem. It may lead to potential exposure of sensitive information like configuration files, credentials, and confidential data. Label Studio versions before 1.16.0 specified SDK versions prior to 1.0.10 as dependencies, and the issue was confirmed in Label Studio version 1.13.2.dev0; therefore, Label Studio users should upgrade to 1.16.0 or newer to mitigate it.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`ChoCVE-2024-26152 · Other software · HumanSignal · reported by GitHubMedium 4.7
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project.  2. Upload a file containing the payload using the "Upload Files" function. 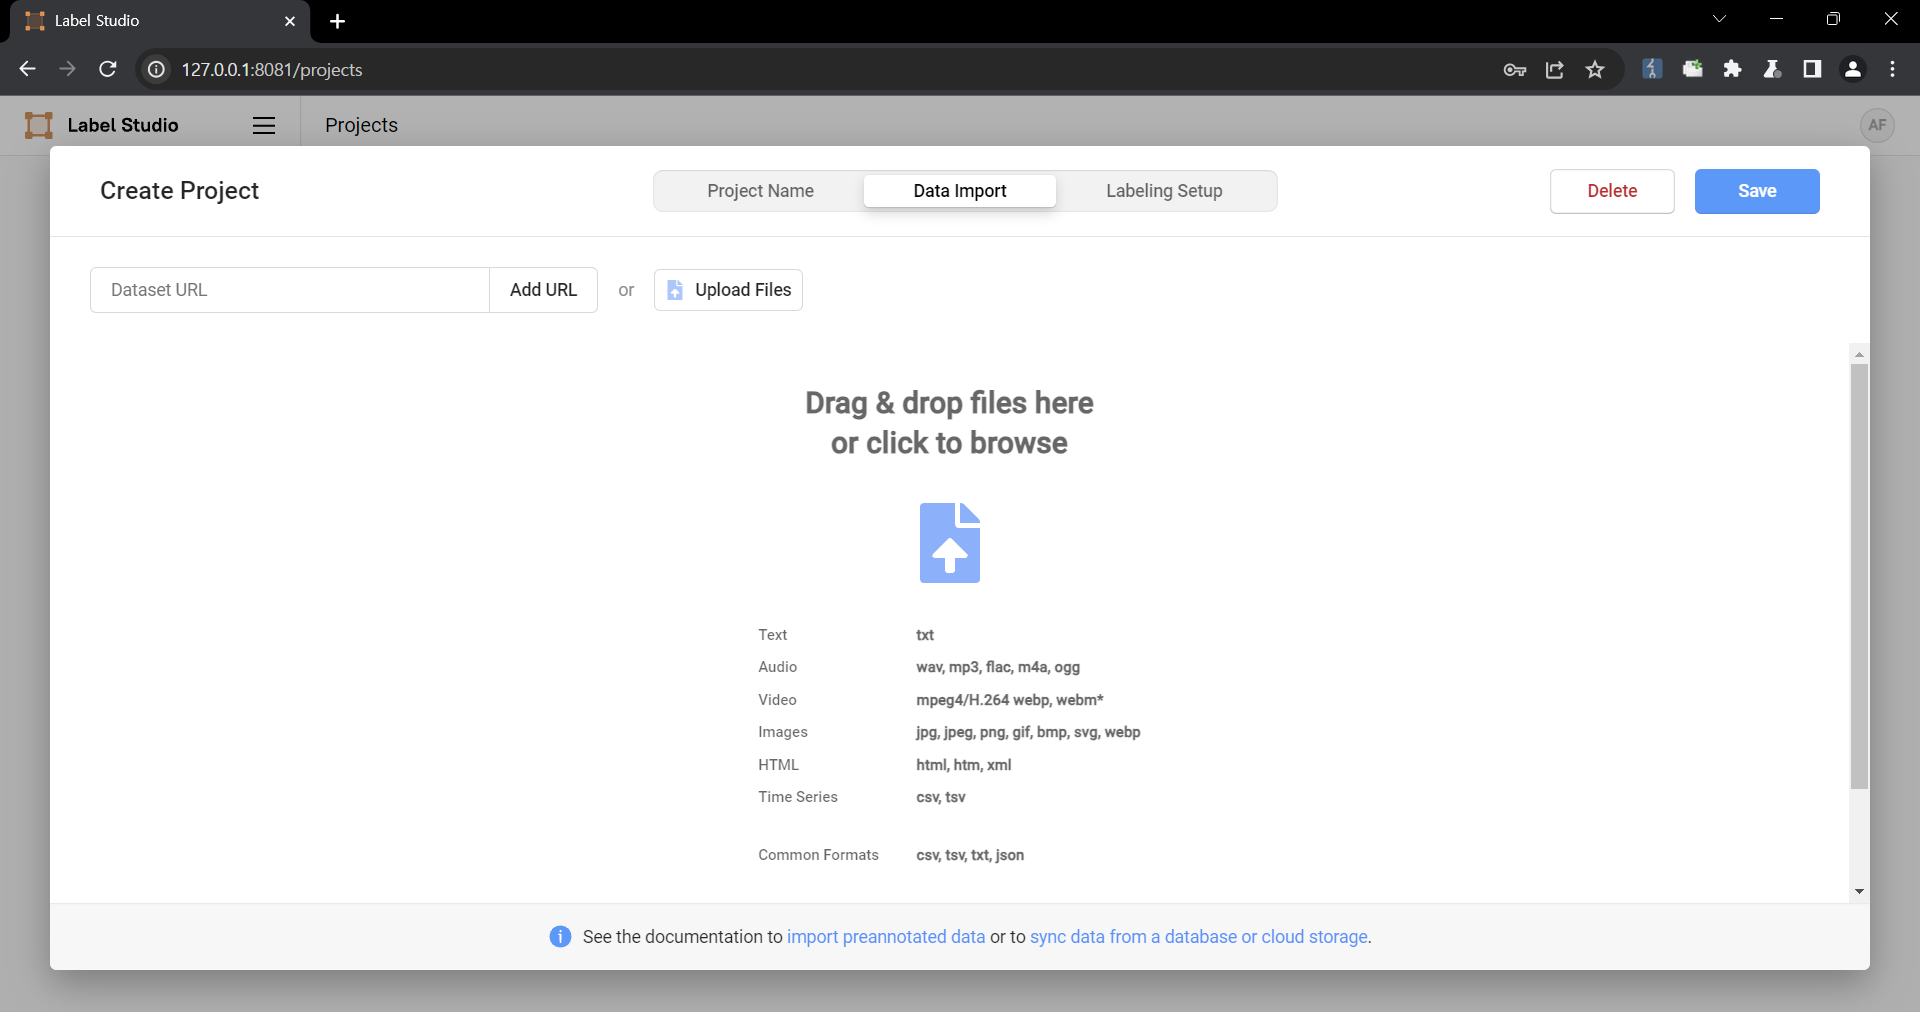 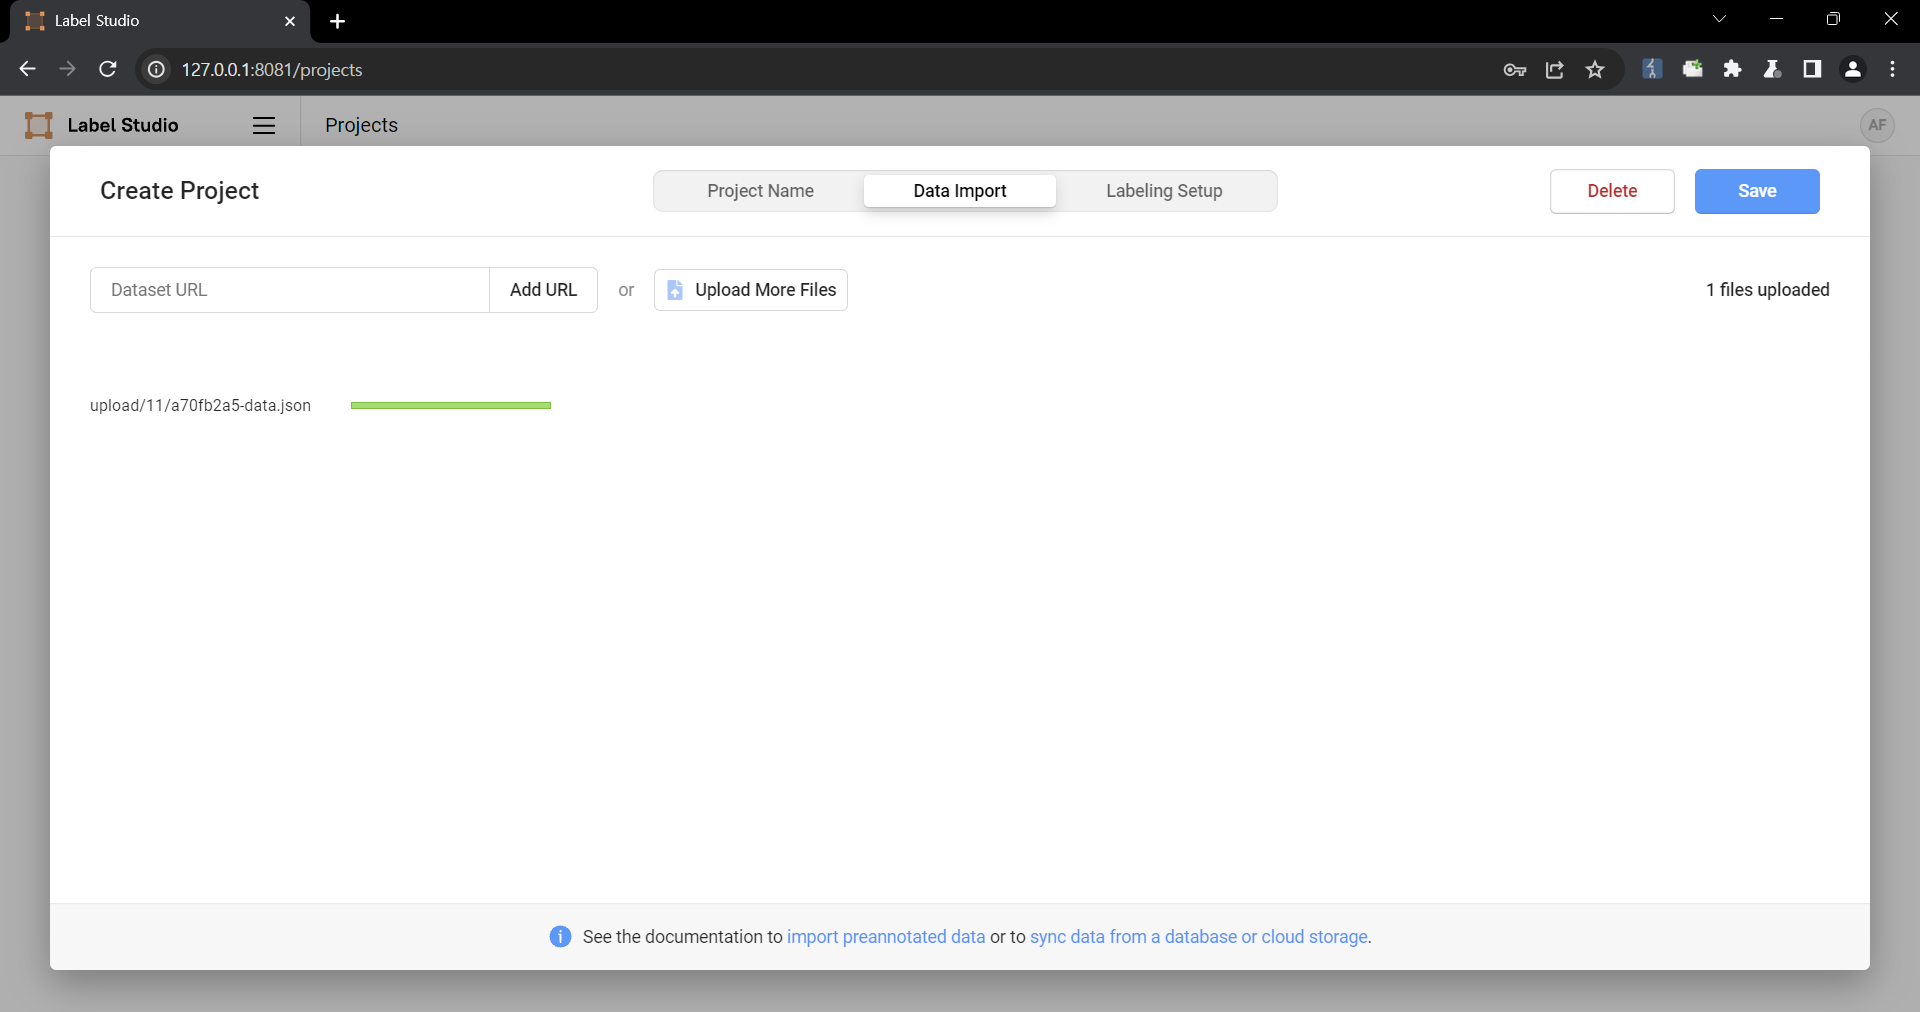 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 31, 2024Label Studio is a popular open source data labeling tool.CVE-2023-47116 · Other software · HumanSignal · reported by GitHubMedium 5.3
Label Studio is a popular open source data labeling tool. The vulnerability affects all versions of Label Studio prior to 1.11.0 and was tested on version 1.8.2. Label Studio's SSRF protections that can be enabled by setting the `SSRF_PROTECTION_ENABLED` environment variable can be bypassed to access internal web servers. This is because the current SSRF validation is done by executing a single DNS lookup to verify that the IP address is not in an excluded subnet range. This protection can be bypassed by either using HTTP redirection or performing a DNS rebinding attack.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 23, 2024Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and couldCVE-2024-23633 · Other software · HumanSignal · reported by GitHubMedium 4.7
Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and could be viewed on the website. Prior to version 1.10.1, this feature could had been abused to download a HTML file that executed malicious JavaScript code in the context of the Label Studio website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. `data_import/uploader.py` lines 125C5 through 146 showed that if a URL passed the server side request forgery verification checks, the contents of the file would be downloaded using the filename in the URL. The downloaded file path could then be retrieved by sending a request to `/api/projects/{project_id}/file-uploads?ids=[{download_id}]` where `{project_id}` was the ID of the project and `{download_id}` was the ID of the downloaded file. Once the downloaded file path was retrieved by the previous API endpoint, `data_import/api.py`lines
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddeveloper.mozilla.orggithub.com
Jan 23, 2024Label Studio is an a popular open source data labeling tool.CVE-2023-47115 · Other software · HumanSignal · reported by GitHubHigh 7.1
Label Studio is an a popular open source data labeling tool. Versions prior to 1.9.2 have a cross-site scripting (XSS) vulnerability that could be exploited when an authenticated user uploads a crafted image file for their avatar that gets rendered as a HTML file on the website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. The file `users/functions.py` lines 18-49 show that the only verification check is that the file is an image by extracting the dimensions from the file. Label Studio serves avatar images using Django's built-in `serve` view, which is not secure for production use according to Django's documentation. The issue with the Django `serve` view is that it determines the `Content-Type` of the response by the file extension in the URL path. Therefore, an attacker can upload an image that contains malicious HTML code and name the file with a `.html` extension to be rendered as a HTML page. The only file extension validat
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocs.djangoproject.comgithub.com
Nov 13, 2023Label Studio is an open source data labeling tool.CVE-2023-47117 · Other software · HumanSignal · reported by GitHubHigh 7.5
Label Studio is an open source data labeling tool. In all current versions of Label Studio prior to 1.9.2post0, the application allows users to insecurely set filters for filtering tasks. An attacker can construct a filter chain to filter tasks based on sensitive fields for all user accounts on the platform by exploiting Django's Object Relational Mapper (ORM). Since the results of query can be manipulated by the ORM filter, an attacker can leak these sensitive fields character by character. In addition, Label Studio had a hard coded secret key that an attacker can use to forge a session token of any user by exploiting this ORM Leak vulnerability to leak account password hashes. This vulnerability has been addressed in commit `f931d9d129` which is included in the 1.9.2post0 release. Users are advised to upgrade. There are no known workarounds for this vulnerability.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Nov 9, 2023Label Studio is a multi-type data labeling and annotation tool with standardized output format.CVE-2023-43791 · Other software · HumanSignal · reported by GitHubCritical 9.8
Label Studio is a multi-type data labeling and annotation tool with standardized output format. There is a vulnerability that can be chained within the ORM Leak vulnerability to impersonate any account on Label Studio. An attacker could exploit these vulnerabilities to escalate their privileges from a low privilege user to a Django Super Administrator user. The vulnerability was found to affect versions before `1.8.2`, where a patch was introduced.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Oct 3, 2022A Server Side Request Forgery (SSRF) in the Data Import module in Heartex - Label Studio Community Edition versions 1.5.0 and earlier allows an authenticated usCVE-2022-36551 · Other software · Heartex · reported by MITREMedium 6.5
A Server Side Request Forgery (SSRF) in the Data Import module in Heartex - Label Studio Community Edition versions 1.5.0 and earlier allows an authenticated user to access arbitrary files on the system. Furthermore, self-registration is enabled by default in these versions of Label Studio enabling a remote attacker to create a new account and then exploit the SSRF.
- Product
- Label Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordlabelstud.iopacketstormsecurity.com
Where this comes from: the exploited list is CISA’s Known Exploited Vulnerabilities catalog. Everything else is the whole National Vulnerability Database, where each record is published by the team that found the bug (Wordfence, Patchstack, WPScan, the vendors themselves and others); we show who. Exploit odds are FIRST’s EPSS, updated daily. Titles and categories are ours, so check the linked record before acting on a detail. For a write-up of the big ones, see our advisories. Every vendor, and every WordPress plugin and theme with a recorded flaw, also has its own page. All of it is free to reuse as JSON, CSV or RSS.
Weekly security brief
The flaws that hit local websites, every Friday.
One short email: what got exploited this week, which WordPress plugins broke, and what to check. Unsubscribe in one click.
Tell us what you're building.
A website, your marketing, a security check, an app, or the thing you've been running out of a spreadsheet for three years. A few lines is plenty.
Not ready to talk yet? Run the free website check and see what Google sees.