Vulnerability database
Every flaw the U.S. government’s cybersecurity agency (CISA) has confirmed attackers are using, plus the new WordPress plugin and theme bugs published each day, sorted by what they mean for a small business. We refresh it twice a day. If you see something your website or office runs, tell us.
3,383 results · page 31 of 68
Feb 28, 2024The EmbedPress – Embed PDF, YouTube, Google Docs, Vimeo, Wistia Videos, Audios, Maps & Any Documents in Gutenberg & Elementor plugin for WordPress is vulnerableCVE-2024-1349 · WordPress plugins & themes · reported by WordfenceMedium 6.4
The EmbedPress – Embed PDF, YouTube, Google Docs, Vimeo, Wistia Videos, Audios, Maps & Any Documents in Gutenberg & Elementor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin's shortcode(s) in all versions up to, and including, 3.9.8 due to insufficient input sanitization and output escaping on user supplied attributes. This makes it possible for authenticated attackers with contributor-level and above permissions to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Affected
- up to 3.9.8
- What to do
- Affects up to 3.9.8. Update the plugin to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgplugins.trac.wordpress.org
Feb 26, 2024A DOM based cross-site scripting (XSS) vulnerability in the component /beep/Beep.Instrument.js of stewdio beep.js before commit ef22ad7 allows attackers to execCVE-2024-26465 · Other software · reported by MITREMedium 6.1
A DOM based cross-site scripting (XSS) vulnerability in the component /beep/Beep.Instrument.js of stewdio beep.js before commit ef22ad7 allows attackers to execute arbitrary Javascript via sending a crafted URL.
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgist.github.comgist.github.com
Feb 22, 2024### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`ChoCVE-2024-26152 · Other software · HumanSignal · reported by GitHubMedium 4.7
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 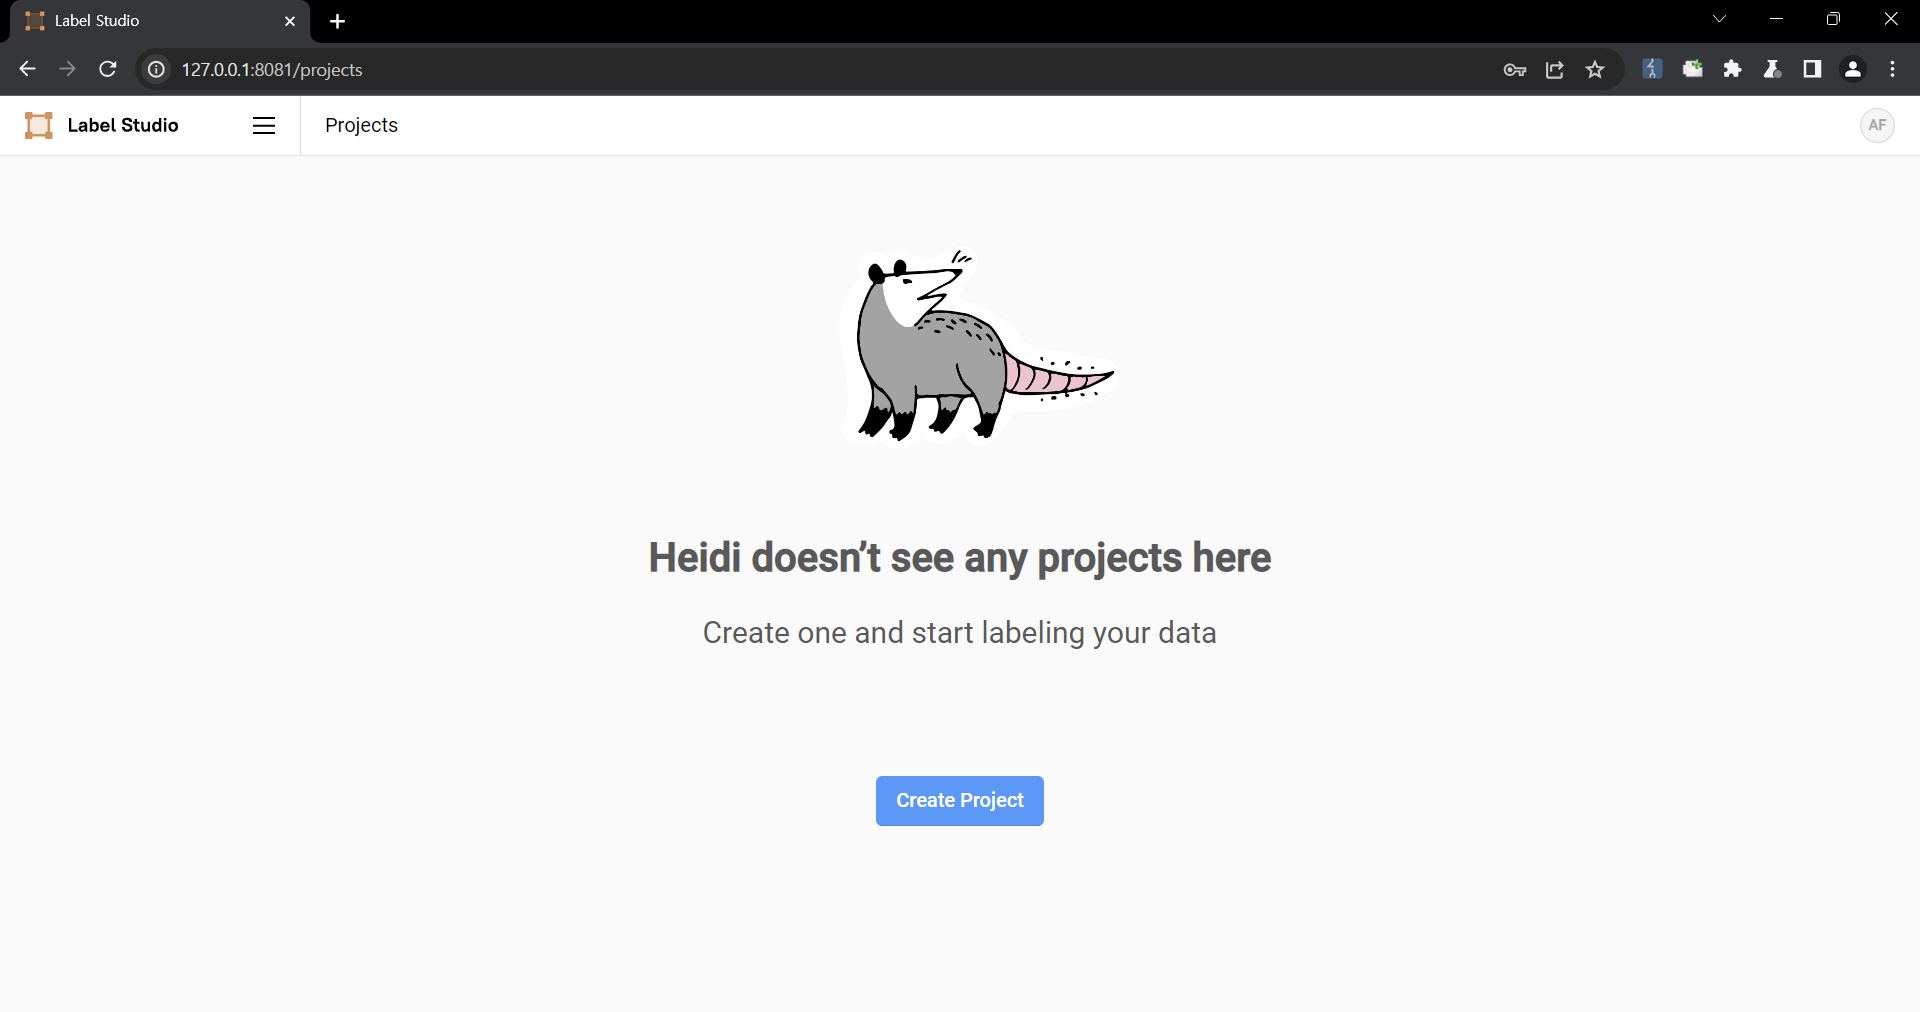 2. Upload a file containing the payload using the "Upload Files" function. 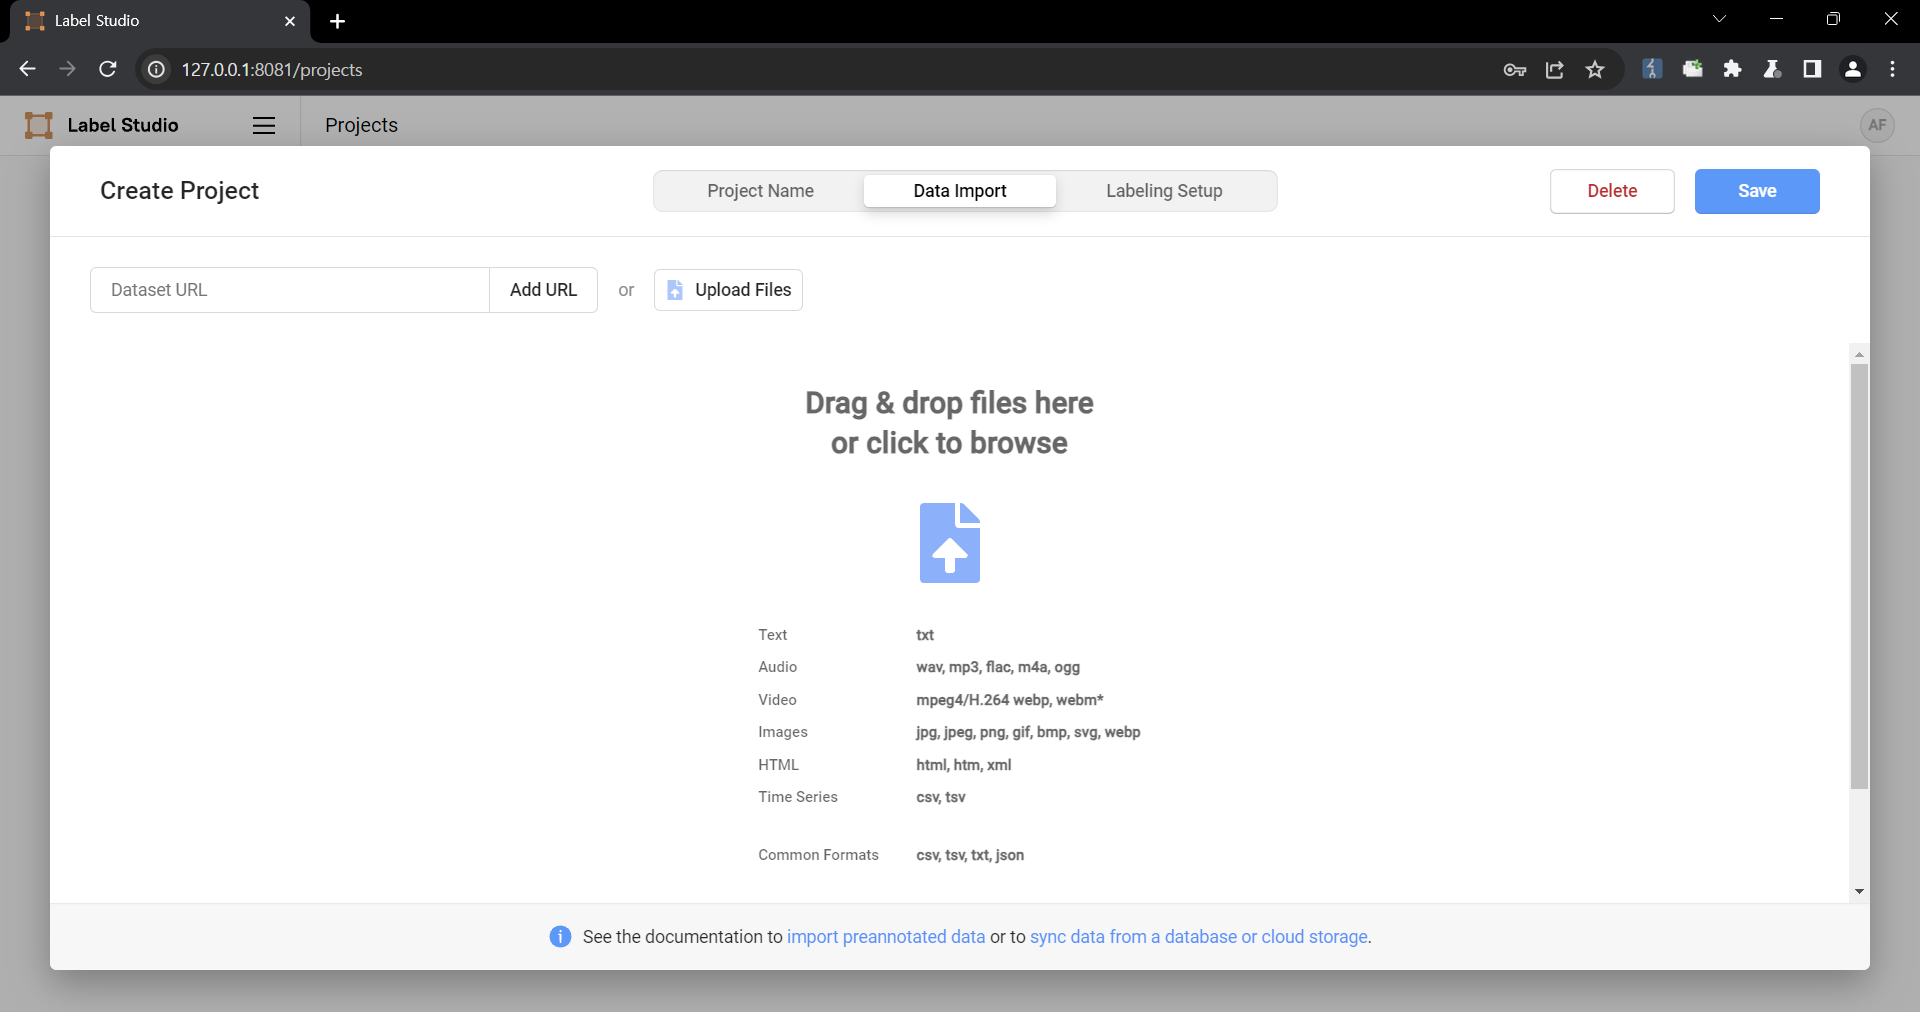 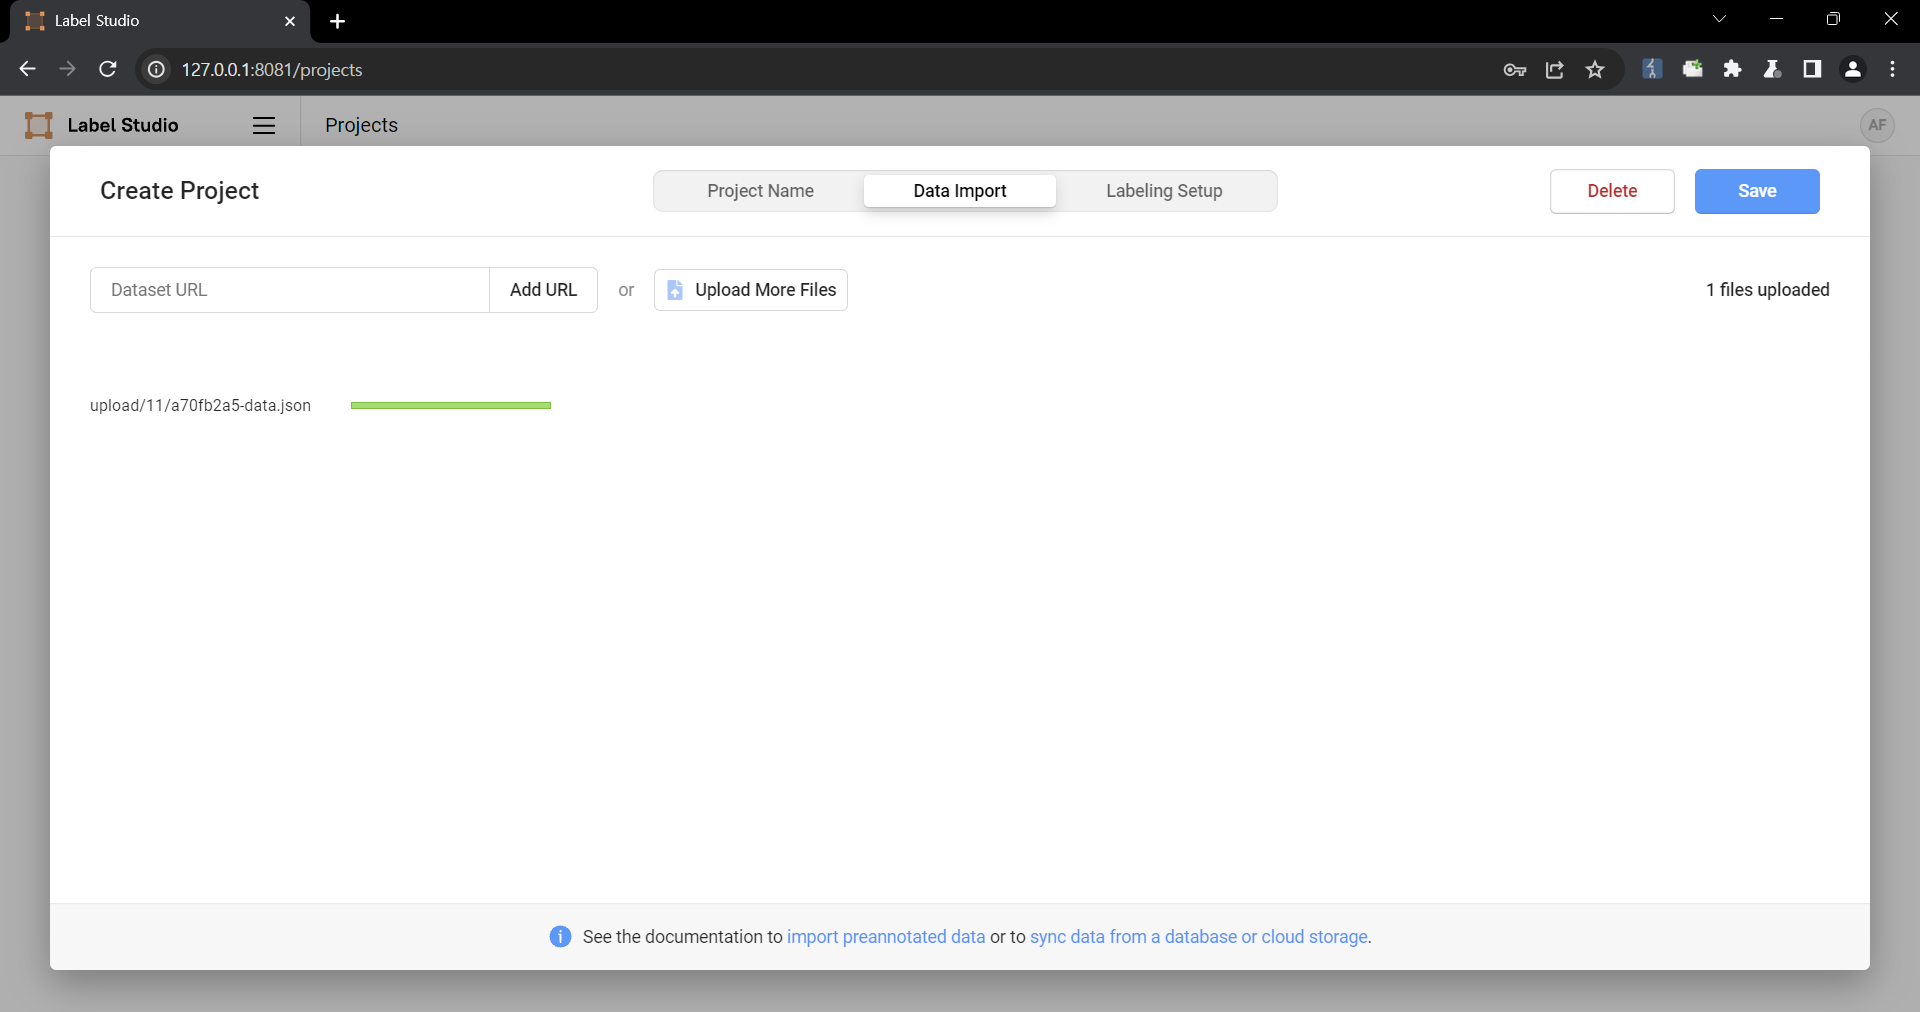 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024A reflected Cross-Site Scripting (XSS) vulnerability in FUEL CMS 1.5.2allows attackers to run arbitrary code via crafted string after the group_id parameter.CVE-2024-25369 · Other software · Thedaylightstudio · reported by MITREMedium 5.4
A reflected Cross-Site Scripting (XSS) vulnerability in FUEL CMS 1.5.2allows attackers to run arbitrary code via crafted string after the group_id parameter.
- Product
- Fuel CMS
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024B&R Automation Studio Upgrade Service and B&R Technology Guarding use insufficient cryptography for communication to the upgrade and the licensing servers.CVE-2024-0220 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 8.3
B&R Automation Studio Upgrade Service and B&R Technology Guarding use insufficient cryptography for communication to the upgrade and the licensing servers. A network-based attacker could exploit the vulnerability to execute arbitrary code on the products or sniff sensitive data.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 17, 2024Vulnerability of configuration defects in some APIs of the audio module.Successful exploitation of this vulnerability may affect availability.CVE-2023-52358 · Other software · Huawei · reported by psirt@huawei.comMedium 6.2
Vulnerability of configuration defects in some APIs of the audio module.Successful exploitation of this vulnerability may affect availability.
- Product
- HarmonyOS
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordconsumer.huawei.comdevice.harmonyos.com
Feb 16, 2024In onActivityResult of NotificationSoundPreference.java, there is a possible way to hear audio files belonging to a different user due to a confused deputy.CVE-2024-0020 · Computers, phones & browsers · Google · reported by security@android.comMedium 5.5
In onActivityResult of NotificationSoundPreference.java, there is a possible way to hear audio files belonging to a different user due to a confused deputy. This could lead to local information disclosure across users of a device with no additional execution privileges needed. User interaction is not needed for exploitation.
- Product
- Android
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordandroid.googlesource.comsource.android.com
Feb 15, 2024A XSLT Server Side injection vulnerability in the Import Jobs function of FireBear Improved Import And Export v3.8.6 allows attackers to execute arbitrary commaCVE-2024-25413 · Other software · firebear_studio · reported by MITREHigh 7.2
A XSLT Server Side injection vulnerability in the Import Jobs function of FireBear Improved Import And Export v3.8.6 allows attackers to execute arbitrary commands via a crafted XSLT file.
- Product
- improved_import_and_export
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgithub.compacketstormsecurity.com
Feb 6, 2024Unrestricted File Upload vulnerability in iSpyConnect.com Agent DVR 5.1.6.0 allows attackers to upload arbitrary files via the upload audio component.CVE-2024-22515 · Other software · Ispyconnect · reported by MITREHigh 8.8
Unrestricted File Upload vulnerability in iSpyConnect.com Agent DVR 5.1.6.0 allows attackers to upload arbitrary files via the upload audio component.
- Product
- Agent DVR
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 6, 2024Memory corruption in Audio while processing the calibration data returned from ACDB loader.CVE-2023-33069 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comMedium 6.7
Memory corruption in Audio while processing the calibration data returned from ACDB loader.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Feb 6, 2024Memory corruption in Audio while processing IIR config data from AFE calibration block.CVE-2023-33068 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comMedium 6.7
Memory corruption in Audio while processing IIR config data from AFE calibration block.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Feb 6, 2024Memory corruption in Audio while calling START command on host voice PCM multiple times for the same RX or TX tap points.CVE-2023-33067 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comMedium 6.7
Memory corruption in Audio while calling START command on host voice PCM multiple times for the same RX or TX tap points.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Feb 6, 2024Information disclosure in Audio while accessing AVCS services from ADSP payload.CVE-2023-33065 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comMedium 6.1
Information disclosure in Audio while accessing AVCS services from ADSP payload.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Feb 6, 2024Transient DOS in Audio when invoking callback function of ASM driver.CVE-2023-33064 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comMedium 5.5
Transient DOS in Audio when invoking callback function of ASM driver.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Feb 5, 2024A local file include could be remotely triggered in Gradio due to a vulnerable user-supplied JSON value in an API request.CVE-2024-0964 · Other software · gradio-app · reported by security@huntr.devCritical 9.4
A local file include could be remotely triggered in Gradio due to a vulnerable user-supplied JSON value in an API request.
- Product
- gradio-app/gradio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 5, 2024Content Views – Post Grid, Slider, Accordion (Gutenberg Blocks and Shortcode): Stored Cross-Site ScriptingCVE-2024-0612 · WordPress plugins & themes · reported by WordfenceMedium 4.4
The Content Views – Post Grid, Slider, Accordion (Gutenberg Blocks and Shortcode) plugin for WordPress is vulnerable to Stored Cross-Site Scripting via admin settings in all versions up to, and including, 3.6.2 due to insufficient input sanitization and output escaping. This makes it possible for authenticated attackers, with administrator-level permissions and above, to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page. This only affects multi-site installations and installations where unfiltered_html has been disabled.
- Product
- Content Views – Post Grid, Slider, Accordion (Gutenberg Blocks and Shortcode)
- Affected
- up to 3.6.2
- What to do
- Affects up to 3.6.2. Update Content Views – Post Grid, Slider, Accordion (Gutenberg Blocks and Shortcode) to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordadvisory.abay.shplugins.trac.wordpress.org
Feb 2, 2024: Relative Path Traversal vulnerability in B&R Industrial Automation Automation Studio allows Relative Path Traversal.This issue affects Automation Studio: fromCVE-2021-22281 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comMedium 6.3
: Relative Path Traversal vulnerability in B&R Industrial Automation Automation Studio allows Relative Path Traversal.This issue affects Automation Studio: from 4.0 through 4.12.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 2, 2024Unquoted Search Path or Element vulnerability in B&R Industrial Automation Automation Studio, B&R Industrial Automation NET/PVI allows Target Programs with ElevCVE-2020-24682 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 7.2
Unquoted Search Path or Element vulnerability in B&R Industrial Automation Automation Studio, B&R Industrial Automation NET/PVI allows Target Programs with Elevated Privileges.This issue affects Automation Studio: from 4.0 through 4.6, from 4.7.0 before 4.7.7 SP, from 4.8.0 before 4.8.6 SP, from 4.9.0 before 4.9.4 SP; NET/PVI: from 4.0 through 4.6, from 4.7.0 before 4.7.7, from 4.8.0 before 4.8.6, from 4.9.0 before 4.9.4.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 2, 2024Improper Control of Generation of Code ('Code Injection') vulnerability in B&R Industrial Automation Automation Studio allows Local Execution of Code.This issueCVE-2021-22282 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 8.3
Improper Control of Generation of Code ('Code Injection') vulnerability in B&R Industrial Automation Automation Studio allows Local Execution of Code.This issue affects Automation Studio: from 4.0 through 4.12.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 2, 2024Incorrect Permission Assignment for Critical Resource vulnerability in B&R Industrial Automation Automation Studio allows Privilege Escalation.This issue affectCVE-2020-24681 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 8.2
Incorrect Permission Assignment for Critical Resource vulnerability in B&R Industrial Automation Automation Studio allows Privilege Escalation.This issue affects Automation Studio: from 4.6.0 through 4.6.X, from 4.7.0 before 4.7.7 SP, from 4.8.0 before 4.8.6 SP, from 4.9.0 before 4.9.4 SP.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 1, 2024 When SEW-EURODRIVE MOVITOOLS MotionStudio processes XML information unrestricted file access can occur.CVE-2024-1167 · Other software · SEW-EURODRIVE · reported by ics-cert@hq.dhs.govMedium 5.5
When SEW-EURODRIVE MOVITOOLS MotionStudio processes XML information unrestricted file access can occur.
- Product
- MOVITOOLS MotionStudio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordcisa.govseweurodrive.com
Feb 1, 2024An OS Command Injection vulnerability exists in BIOVIA Materials Studio products from Release BIOVIA 2021 through Release BIOVIA 2023.CVE-2023-6078 · Other software · Dassault Systèmes · reported by 3DS.Information-Security@3ds.comHigh 8.8
An OS Command Injection vulnerability exists in BIOVIA Materials Studio products from Release BIOVIA 2021 through Release BIOVIA 2023. Upload of a specially crafted perl script can lead to arbitrary command execution.
- Product
- BIOVIA Materials Studio products
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 31, 2024Label Studio is a popular open source data labeling tool.CVE-2023-47116 · Other software · HumanSignal · reported by GitHubMedium 5.3
Label Studio is a popular open source data labeling tool. The vulnerability affects all versions of Label Studio prior to 1.11.0 and was tested on version 1.8.2. Label Studio's SSRF protections that can be enabled by setting the `SSRF_PROTECTION_ENABLED` environment variable can be bypassed to access internal web servers. This is because the current SSRF validation is done by executing a single DNS lookup to verify that the IP address is not in an excluded subnet range. This protection can be bypassed by either using HTTP redirection or performing a DNS rebinding attack.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 31, 2024In Telerik Test Studio versions prior to v2023.3.1330, a privilege elevation vulnerability has been identified in the applications installer component.CVE-2024-0833 · Other software · Progress Software · reported by security@progress.comHigh 7.8
In Telerik Test Studio versions prior to v2023.3.1330, a privilege elevation vulnerability has been identified in the applications installer component. In an environment where an existing Telerik Test Studio install is present, a lower privileged user has the ability to manipulate the installation package to elevate their privileges on the underlying operating system.
- Product
- Telerik Test Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocs.telerik.comtelerik.com
Jan 26, 2024An issue in kosei entertainment esportsstudioLegends mini-app on Line v13.6.1 allows attackers to send crafted malicious notifications via leakage of the channeCVE-2023-48132 · Other software · Linecorp · reported by MITREMedium 5.4
An issue in kosei entertainment esportsstudioLegends mini-app on Line v13.6.1 allows attackers to send crafted malicious notifications via leakage of the channel access token.
- Product
- Line
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 25, 2024A vulnerability classified as problematic was found in Poikosoft EZ CD Audio Converter 8.0.7.CVE-2024-0886 · Other software · Poikosoft · reported by VulDBLow 3.3
A vulnerability classified as problematic was found in Poikosoft EZ CD Audio Converter 8.0.7. Affected by this vulnerability is an unknown functionality of the component Activation Handler. The manipulation of the argument Key leads to denial of service. Local access is required to approach this attack. The exploit has been disclosed to the public and may be used. The identifier VDB-252037 was assigned to this vulnerability.
- Product
- EZ CD Audio Converter
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 23, 2024Ubuntu's pipewire-pulse in snap grants microphone access even when the snap interface for audio-record is not set.CVE-2022-4964 · Other software · Canonical Ltd. · reported by security@ubuntu.comMedium 5.5
Ubuntu's pipewire-pulse in snap grants microphone access even when the snap interface for audio-record is not set.
- Product
- Ubuntu pipewire-pulse
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbugs.launchpad.netcve.mitre.org
Jan 23, 2024Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and couldCVE-2024-23633 · Other software · HumanSignal · reported by GitHubMedium 4.7
Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and could be viewed on the website. Prior to version 1.10.1, this feature could had been abused to download a HTML file that executed malicious JavaScript code in the context of the Label Studio website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. `data_import/uploader.py` lines 125C5 through 146 showed that if a URL passed the server side request forgery verification checks, the contents of the file would be downloaded using the filename in the URL. The downloaded file path could then be retrieved by sending a request to `/api/projects/{project_id}/file-uploads?ids=[{download_id}]` where `{project_id}` was the ID of the project and `{download_id}` was the ID of the downloaded file. Once the downloaded file path was retrieved by the previous API endpoint, `data_import/api.py`lines
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddeveloper.mozilla.orggithub.com
Jan 23, 2024Android Spoon application version 7.11.1 to 8.6.0 uses hard-coded credentials, which may allow a local attacker to retrieve the hard-coded API key when the applCVE-2024-23453 · Other software · Spoon Radio Japan Inc. · reported by vultures@jpcert.or.jpMedium 5.5
Android Spoon application version 7.11.1 to 8.6.0 uses hard-coded credentials, which may allow a local attacker to retrieve the hard-coded API key when the application binary is reverse-engineered. This API key may be used for unexpected access of the associated service.
- Product
- Android Spoon application
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 23, 2024Use after free in Web Audio in Google Chrome prior to 121.0.6167.85 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page.CVE-2024-0807 · Computers, phones & browsers · Google · reported by chrome-cve-admin@google.comHigh 8.8
Use after free in Web Audio in Google Chrome prior to 121.0.6167.85 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page. (Chromium security severity: High)
- Product
- Chrome
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordchromereleases.googleblog.comcrbug.com
Jan 23, 2024Label Studio is an a popular open source data labeling tool.CVE-2023-47115 · Other software · HumanSignal · reported by GitHubHigh 7.1
Label Studio is an a popular open source data labeling tool. Versions prior to 1.9.2 have a cross-site scripting (XSS) vulnerability that could be exploited when an authenticated user uploads a crafted image file for their avatar that gets rendered as a HTML file on the website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. The file `users/functions.py` lines 18-49 show that the only verification check is that the file is an image by extracting the dimensions from the file. Label Studio serves avatar images using Django's built-in `serve` view, which is not secure for production use according to Django's documentation. The issue with the Django `serve` view is that it determines the `Content-Type` of the response by the file extension in the URL path. Therefore, an attacker can upload an image that contains malicious HTML code and name the file with a `.html` extension to be rendered as a HTML page. The only file extension validat
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocs.djangoproject.comgithub.com
Jan 23, 2024The radio frequency communication protocol being used by Meross MSH30Q 4.5.23 is vulnerable to replay attacks, allowing attackers to record and replay previouslCVE-2023-46892 · Other software · meross · reported by MITREHigh 8.8
The radio frequency communication protocol being used by Meross MSH30Q 4.5.23 is vulnerable to replay attacks, allowing attackers to record and replay previously captured communication to execute unauthorized commands or actions (e.g., thermostat's temperature).
- Product
- msh30q
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 23, 2024The WebAudio `OscillatorNode` object was susceptible to a stack buffer overflow.CVE-2024-0745 · Computers, phones & browsers · Mozilla · reported by security@mozilla.orgHigh 8.8
The WebAudio `OscillatorNode` object was susceptible to a stack buffer overflow. This could have led to a potentially exploitable crash. This vulnerability affects Firefox < 122.
- Product
- Firefox
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbugzilla.mozilla.orgmozilla.org
Jan 22, 2024Project files may contain malicious contents which the software will use to create files on the filesystem.CVE-2022-45792 · Other software · Omron · reported by ot-cert@dragos.comHigh 7.8
Project files may contain malicious contents which the software will use to create files on the filesystem. This allows directory traversal and overwriting files with the privileges of the logged-in user.
- Product
- Sysmac Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 17, 2024Studio Network Solutions ShareBrowser before 7.0 on macOS mishandles signature verification, aka PMP-2636.CVE-2023-44077 · Other software · Studionetworksolutions · reported by MITRECritical 9.8
Studio Network Solutions ShareBrowser before 7.0 on macOS mishandles signature verification, aka PMP-2636.
- Product
- Sharebrowser
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordkhronokernel.comsupport.studionetworksolutions.com
Jan 17, 2024A vulnerability in the web-based management interface of the Cisco WAP371 Wireless-AC/N Dual Radio Access Point (AP) with Single Point Setup could allow an authCVE-2024-20287 · Network & remote access · Cisco · reported by psirt@cisco.comMedium 6.5
A vulnerability in the web-based management interface of the Cisco WAP371 Wireless-AC/N Dual Radio Access Point (AP) with Single Point Setup could allow an authenticated, remote attacker to perform command injection attacks against an affected device. This vulnerability is due to improper validation of user-supplied input. An attacker could exploit this vulnerability by sending crafted HTTP requests to the web-based management interface of an affected system. A successful exploit could allow the attacker to execute arbitrary commands with root privileges on the device. To exploit this vulnerability, the attacker must have valid administrative credentials for the device.
- Product
- Cisco Business Wireless Access Point Software
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsec.cloudapps.cisco.comsec.cloudapps.cisco.com
Jan 16, 2024Prior to v176, when opening a new project Meta Spark Studio would execute scripts defined inside of a package.json file included as part of that project.CVE-2024-23347 · Other software · Meta Platforms, Inc · reported by cve-assign@fb.comHigh 7.8
Prior to v176, when opening a new project Meta Spark Studio would execute scripts defined inside of a package.json file included as part of that project. Those scripts would have the ability to execute arbitrary code on the system as the application.
- Product
- Meta Spark Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordfacebook.comfacebook.com
Jan 11, 2024The remote keyless system of the Hozard alarm system (alarmsystemen) v1.0 sends an identical radio frequency signal for each request, which results in an attackCVE-2023-50128 · Other software · Hozard · reported by MITREMedium 5.3
The remote keyless system of the Hozard alarm system (alarmsystemen) v1.0 sends an identical radio frequency signal for each request, which results in an attacker being able to conduct replay attacks to bring the alarm system to a disarmed state.
- Product
- Alarm System
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 10, 2024Sysmac Studio installs executables in a directory with poor permissions.CVE-2022-45793 · Other software · Omron · reported by ot-cert@dragos.comMedium 5.5
Sysmac Studio installs executables in a directory with poor permissions. This can allow a locally-authenticated attacker to overwrite files which will result in code execution with privileges of a different user.
- Product
- Sysmac Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 9, 2024 A CWE-502: Deserialization of untrusted data vulnerability exists that could allow an attacker logged in with a user level account to gain higher privileges byCVE-2023-7032 · Other software · Schneider Electric · reported by cybersecurity@se.comHigh 7.8
A CWE-502: Deserialization of untrusted data vulnerability exists that could allow an attacker logged in with a user level account to gain higher privileges by providing a harmful serialized object.
- Product
- Easergy Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddownload.schneider-electric.comdownload.schneider-electric.com
Jan 9, 2024Visual Studio Elevation of Privilege VulnerabilityCVE-2024-20656 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.8
Visual Studio Elevation of Privilege Vulnerability
- Product
- Microsoft Visual Studio 2017 version 15.9 (includes 15.0 - 15.8)
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Jan 9, 2024NET, .NET Framework, and Visual Studio Security Feature Bypass VulnerabilityCVE-2024-0057 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comCritical 9.1
NET, .NET Framework, and Visual Studio Security Feature Bypass Vulnerability
- Product
- .NET 8.0
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Jan 8, 2024Dataiku DSS before 11.4.5 and 12.4.1 has Incorrect Access Control that could lead to a full authentication bypass.CVE-2023-51717 · Other software · Dataiku · reported by MITRECritical 9.8
Dataiku DSS before 11.4.5 and 12.4.1 has Incorrect Access Control that could lead to a full authentication bypass.
- Product
- Data Science Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddataiku.comdoc.dataiku.com
Jan 3, 2024Use after free in WebAudio in Google Chrome prior to 120.0.6099.199 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page.CVE-2024-0224 · Computers, phones & browsers · Google · reported by chrome-cve-admin@google.comHigh 8.8
Use after free in WebAudio in Google Chrome prior to 120.0.6099.199 allowed a remote attacker to potentially exploit heap corruption via a crafted HTML page. (Chromium security severity: High)
- Product
- Chrome
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordchromereleases.googleblog.comcrbug.com
Jan 3, 2024The EmbedPress – Embed PDF, YouTube, Google Docs, Vimeo, Wistia Videos, Audios, Maps & Any Documents in Gutenberg & Elementor plugin for WordPress is vulnerableCVE-2023-6986 · WordPress plugins & themes · reported by WordfenceMedium 6.4
The EmbedPress – Embed PDF, YouTube, Google Docs, Vimeo, Wistia Videos, Audios, Maps & Any Documents in Gutenberg & Elementor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin's embed_oembed_html shortcode in all versions up to 3.9.5 (exclusive) due to insufficient input sanitization and output escaping on user supplied attributes. This makes it possible for authenticated attackers with contributor-level and above permissions to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Affected
- up to 3.9.5
- What to do
- Affects up to 3.9.5. Update the plugin to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.svn.wordpress.orgplugins.trac.wordpress.org
Jan 2, 2024A vulnerability, which was classified as problematic, was found in Acumos Design Studio up to 2.0.7.CVE-2018-25097 · Other software · Acumos · reported by VulDBLow 3.5
A vulnerability, which was classified as problematic, was found in Acumos Design Studio up to 2.0.7. Affected is an unknown function. The manipulation leads to cross site scripting. It is possible to launch the attack remotely. Upgrading to version 2.0.8 is able to address this issue. The name of the patch is 0df8a5e8722188744973168648e4c74c69ce67fd. It is recommended to upgrade the affected component. The identifier of this vulnerability is VDB-249420.
- Product
- Design Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 2, 2024 in OpenHarmony v3.2.2 and prior versions allow a local attacker cause multimedia audio crash through modify a released pointer.CVE-2023-49142 · Other software · OpenHarmony · reported by scy@openharmony.ioMedium 4
in OpenHarmony v3.2.2 and prior versions allow a local attacker cause multimedia audio crash through modify a released pointer.
- Product
- OpenHarmony
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 2, 2024Memory corruption in Audio when memory map command is executed consecutively in ADSP.CVE-2023-33120 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comHigh 7.8
Memory corruption in Audio when memory map command is executed consecutively in ADSP.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Jan 2, 2024The session index variable in PCM host voice audio driver initialized before PCM open, accessed during event callback from ADSP and reset during PCM close may lCVE-2023-33110 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comHigh 7.8
The session index variable in PCM host voice audio driver initialized before PCM open, accessed during event callback from ADSP and reset during PCM close may lead to race condition between event callback - PCM close and reset session index causing memory corruption.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Jan 2, 2024Memory corruption in Audio during playback with speaker protection.CVE-2023-33033 · Computers, phones & browsers · Qualcomm, Inc. · reported by product-security@qualcomm.comHigh 8.4
Memory corruption in Audio during playback with speaker protection.
- Product
- Snapdragon
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordqualcomm.comqualcomm.com
Where this comes from: the exploited list is CISA’s Known Exploited Vulnerabilities catalog. Everything else is the whole National Vulnerability Database, where each record is published by the team that found the bug (Wordfence, Patchstack, WPScan, the vendors themselves and others); we show who. Exploit odds are FIRST’s EPSS, updated daily. Titles and categories are ours, so check the linked record before acting on a detail. For a write-up of the big ones, see our advisories. Every vendor, and every WordPress plugin and theme with a recorded flaw, also has its own page. All of it is free to reuse as JSON, CSV or RSS.
Weekly security brief
The flaws that hit local websites, every Friday.
One short email: what got exploited this week, which WordPress plugins broke, and what to check. Unsubscribe in one click.
Tell us what you're building.
A website, your marketing, a security check, an app, or the thing you've been running out of a spreadsheet for three years. A few lines is plenty.
Not ready to talk yet? Run the free website check and see what Google sees.