Vulnerability database
Every flaw the U.S. government’s cybersecurity agency (CISA) has confirmed attackers are using, plus the new WordPress plugin and theme bugs published each day, sorted by what they mean for a small business. We refresh it twice a day. If you see something your website or office runs, tell us.
1,460 results · page 16 of 30
Apr 18, 2024LearnPress Export Import: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')CVE-2024-32588 · WordPress plugins & themes · reported by PatchstackHigh 7.1
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in ThimPress LearnPress Export Import allows Reflected XSS.This issue affects LearnPress Export Import: from n/a through 4.0.3.
- Product
- LearnPress Export Import
- Affected
- up to 4.0.3
- What to do
- Affects up to 4.0.3. Update LearnPress Export Import to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 16, 2024Vulnerability in the Oracle Agile Product Lifecycle Management for Process product of Oracle Supply Chain (component: Data Import).CVE-2024-21091 · Other software · Oracle Corporation · reported by secalert_us@oracle.comMedium 6.5
Vulnerability in the Oracle Agile Product Lifecycle Management for Process product of Oracle Supply Chain (component: Data Import). The supported version that is affected is 6.2.4.2. Easily exploitable vulnerability allows low privileged attacker with network access via HTTP to compromise Oracle Agile Product Lifecycle Management for Process. Successful attacks of this vulnerability can result in unauthorized access to critical data or complete access to all Oracle Agile Product Lifecycle Management for Process accessible data. CVSS 3.1 Base Score 6.5 (Confidentiality impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:L/UI:N/S:U/C:H/I:N/A:N).
- Product
- Agile Product Lifecycle Management for Process
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Apr 16, 2024Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Import Utility).CVE-2024-21088 · Other software · Oracle Corporation · reported by secalert_us@oracle.comHigh 7.5
Vulnerability in the Oracle Production Scheduling product of Oracle E-Business Suite (component: Import Utility). Supported versions that are affected are 12.2.4-12.2.12. Easily exploitable vulnerability allows unauthenticated attacker with network access via HTTP to compromise Oracle Production Scheduling. Successful attacks of this vulnerability can result in unauthorized creation, deletion or modification access to critical data or all Oracle Production Scheduling accessible data. CVSS 3.1 Base Score 7.5 (Integrity impacts). CVSS Vector: (CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:N/I:H/A:N).
- Product
- Production Scheduling
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Apr 15, 2024Import Users from CSV: Deserialization of Untrusted DataCVE-2024-32431 · WordPress plugins & themes · reported by PatchstackMedium 4.4
Deserialization of Untrusted Data vulnerability in WP All Import Import Users from CSV.This issue affects Import Users from CSV: from n/a through 1.2.
- Product
- Import Users from CSV
- Affected
- up to 1.2
- What to do
- Affects up to 1.2. Update Import Users from CSV to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 12, 2024WordPress Comments Import & Export: Cross-Site Request Forgery (CSRF)CVE-2024-31235 · WordPress plugins & themes · reported by PatchstackMedium 4.3
Cross-Site Request Forgery (CSRF) vulnerability in WebToffee WordPress Comments Import & Export.This issue affects WordPress Comments Import & Export: from n/a through 2.3.5.
- Product
- WordPress Comments Import & Export
- Affected
- up to 2.3.5
- What to do
- Affects up to 2.3.5. Update WordPress Comments Import & Export to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 10, 2024Import any XML or CSV File to: Cross-Site Request Forgery (CSRF)CVE-2024-31939 · WordPress plugins & themes · reported by PatchstackMedium 4.3
Cross-Site Request Forgery (CSRF) vulnerability in Soflyy Import any XML or CSV File to WordPress.This issue affects Import any XML or CSV File to WordPress: from n/a through 3.7.3.
- Product
- Import any XML or CSV File to
- Affected
- up to 3.7.3
- What to do
- Affects up to 3.7.3. Update Import any XML or CSV File to to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 10, 2024The plugin is vulnerable to PHP Object Injection in versions up to and including, 2.6.3 via deserialization of untrusted input in the import function via the 'sCVE-2024-3020 · WordPress plugins & themes · reported by WordfenceHigh 7.2
The plugin is vulnerable to PHP Object Injection in versions up to and including, 2.6.3 via deserialization of untrusted input in the import function via the 'shortcode' parameter. This allows authenticated attackers, with administrator-level access to inject a PHP Object. If a POP chain is present via an additional plugin or theme installed on the target system, it could allow the attacker to delete arbitrary files, retrieve sensitive data, or execute code.
- Affected
- up to 2.6.3
- What to do
- Affects up to 2.6.3. Update the plugin to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgwordfence.com
Apr 9, 2024Template Kit – Import: Stored Cross-Site ScriptingCVE-2024-2334 · WordPress plugins & themes · reported by WordfenceMedium 6.4
The Template Kit – Import plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the template upload functionality in all versions up to, and including, 1.0.14 due to insufficient input sanitization and output escaping. This makes it possible for authenticated attackers, with author access and above, to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Product
- Template Kit – Import
- Affected
- up to 1.0.14
- What to do
- Affects up to 1.0.14. Update Template Kit – Import to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgplugins.trac.wordpress.org
Apr 8, 2024The NMAP Importer service may expose data store credentials to authorized users of the Windows Registry.CVE-2024-23584 · Other software · HCL Software · reported by psirt@hcl.comMedium 6.6
The NMAP Importer service may expose data store credentials to authorized users of the Windows Registry.
- Product
- BigFix Enterprise Suite Asset Discovery
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordsupport.hcltechsw.comsupport.hcltechsw.com
Apr 7, 2024WP Import Export Lite: Deserialization of Untrusted DataCVE-2024-31308 · WordPress plugins & themes · reported by PatchstackMedium 4.4
Deserialization of Untrusted Data vulnerability in VJInfotech WP Import Export Lite.This issue affects WP Import Export Lite: from n/a through 3.9.26.
- Product
- WP Import Export Lite
- Affected
- up to 3.9.26
- What to do
- Affects up to 3.9.26. Update WP Import Export Lite to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 7, 2024Import XML and RSS Feeds: Unrestricted Upload of File with Dangerous TypeCVE-2024-31292 · WordPress plugins & themes · reported by PatchstackHigh 7.2
Unrestricted Upload of File with Dangerous Type vulnerability in Moove Agency Import XML and RSS Feeds.This issue affects Import XML and RSS Feeds: from n/a through 2.1.5.
- Product
- Import XML and RSS Feeds
- Affected
- up to 2.1.5
- What to do
- Affects up to 2.1.5. Update Import XML and RSS Feeds to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 7, 2024LearnPress Export Import: Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection')CVE-2024-31241 · WordPress plugins & themes · reported by PatchstackHigh 7.6
Improper Neutralization of Special Elements used in an SQL Command ('SQL Injection') vulnerability in ThimPress LearnPress Export Import.This issue affects LearnPress Export Import: from n/a through 4.0.3.
- Product
- LearnPress Export Import
- Affected
- up to 4.0.3
- What to do
- Affects up to 4.0.3. Update LearnPress Export Import to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Apr 2, 2024An issue was discovered in seeyonOA version 8, allows remote attackers to execute arbitrary code via the importProcess method in WorkFlowDesignerController.clasCVE-2024-29276 · Other software · seeyonao · reported by MITRECritical 9.8
An issue was discovered in seeyonOA version 8, allows remote attackers to execute arbitrary code via the importProcess method in WorkFlowDesignerController.class component.
- Product
- seeyonoa
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordcnblogs.comcnblogs.com
Mar 29, 2024Import Export WordPress Users: Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal')CVE-2024-30492 · WordPress plugins & themes · reported by PatchstackMedium 4.3
Improper Limitation of a Pathname to a Restricted Directory ('Path Traversal') vulnerability in WebToffee Import Export WordPress Users.This issue affects Import Export WordPress Users: from n/a through 2.5.2.
- Product
- Import Export WordPress Users
- Affected
- up to 2.5.2
- What to do
- Affects up to 2.5.2. Update Import Export WordPress Users to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Mar 27, 2024WordPress Importer: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')CVE-2024-30201 · WordPress plugins & themes · reported by PatchstackHigh 7.1
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in Xylus Themes WordPress Importer allows Reflected XSS.This issue affects WordPress Importer: from n/a through 1.0.4.
- Product
- WordPress Importer
- Affected
- up to 1.0.4
- What to do
- Affects up to 1.0.4. Update WordPress Importer to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Mar 26, 2024Product Import Export for WooCommerce: Unrestricted Upload of File with Dangerous TypeCVE-2024-30231 · WordPress plugins & themes · reported by PatchstackCritical 9.1
Unrestricted Upload of File with Dangerous Type vulnerability in WebToffee Product Import Export for WooCommerce.This issue affects Product Import Export for WooCommerce: from n/a through 2.4.1.
- Product
- Product Import Export for WooCommerce
- Affected
- up to 2.4.1
- What to do
- Affects up to 2.4.1. Update Product Import Export for WooCommerce to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Mar 20, 2024Olive One Click Demo Import: Missing AuthorizationCVE-2024-2702 · WordPress plugins & themes · reported by PatchstackHigh 8.2
Missing Authorization vulnerability in Olive Themes Olive One Click Demo Import allows importing settings and data, ultimately leading to XSS.This issue affects Olive One Click Demo Import: from n/a through 1.1.1.
- Product
- Olive One Click Demo Import
- Affected
- up to 1.1.1
- What to do
- Affects up to 1.1.1. Update Olive One Click Demo Import to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Mar 13, 2024JFrog Artifactory versions below 7.77.7, 7.82.1, are vulnerable to DOM-based cross-site scripting due to improper handling of the import override mechanism.CVE-2024-2247 · Other software · JFrog · reported by reefs@jfrog.comHigh 8.8
JFrog Artifactory versions below 7.77.7, 7.82.1, are vulnerable to DOM-based cross-site scripting due to improper handling of the import override mechanism.
- Product
- Artifactory
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Mar 3, 2024SQL Injection vulnerability in MyPrestaModules "Product Catalog (CSV, Excel) Import" (simpleimportproduct) modules for PrestaShop versions 6.5.0 and before, allCVE-2024-25847 · Other software · myprestamodules · reported by MITRECritical 9.8
SQL Injection vulnerability in MyPrestaModules "Product Catalog (CSV, Excel) Import" (simpleimportproduct) modules for PrestaShop versions 6.5.0 and before, allows attackers to escalate privileges and obtain sensitive information via Send::__construct() and importProducts::_addDataToDb methods.
- Product
- product_catalog_import_for_prestashop
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 29, 2024Apache Airflow, versions before 2.8.2, has a vulnerability that allows authenticated users to view DAG code and import errors of DAGs they do not have permissioCVE-2024-27906 · Websites & servers · Apache Software Foundation · reported by security@apache.orgMedium 5.9
Apache Airflow, versions before 2.8.2, has a vulnerability that allows authenticated users to view DAG code and import errors of DAGs they do not have permission to view through the API and the UI. Users of Apache Airflow are recommended to upgrade to version 2.8.2 or newer to mitigate the risk associated with this vulnerability
- Product
- Apache Airflow
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 28, 2024A low privilege authenticated user could import an existing dashboard or chart that they do not have access to and then modify its metadata, thereby gaining ownCVE-2024-26016 · Websites & servers · Apache Software Foundation · reported by security@apache.orgMedium 4.3
A low privilege authenticated user could import an existing dashboard or chart that they do not have access to and then modify its metadata, thereby gaining ownership of the object. However, it's important to note that access to the analytical data of these charts and dashboards would still be subject to validation based on data access privileges. This issue affects Apache Superset: before 3.0.4, from 3.1.0 before 3.1.1.Users are recommended to upgrade to version 3.1.1, which fixes the issue.
- Product
- Apache Superset
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordopenwall.comlists.apache.org
Feb 27, 2024In the module "Product Catalog (CSV, Excel) Import" (simpleimportproduct) <= 6.7.0 from MyPrestaModules for PrestaShop, a guest can upload files with extensionsCVE-2024-25846 · Other software · myprestamodules · reported by MITRECritical 9.1
In the module "Product Catalog (CSV, Excel) Import" (simpleimportproduct) <= 6.7.0 from MyPrestaModules for PrestaShop, a guest can upload files with extensions .php.
- Product
- simpleimportproduct
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordaddons.prestashop.comsecurity.friendsofpresta.org
Feb 27, 2024In the module "Import/Update Bulk Product from any Csv/Excel File Pro" (ba_importer) up to version 1.1.28 from Buy Addons for PrestaShop, a guest can perform SQCVE-2024-25843 · Other software · communitydeveloper · reported by MITRECritical 9.8
In the module "Import/Update Bulk Product from any Csv/Excel File Pro" (ba_importer) up to version 1.1.28 from Buy Addons for PrestaShop, a guest can perform SQL injection in affected versions.
- Product
- import\/update_bulk_product_from_any_csv\/excel_file_pro
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordaddons.prestashop.comsecurity.friendsofpresta.org
Feb 26, 2024With the following crawler configuration: ```python from bs4 import BeautifulSoup as Soup url = "https://example.com" loader = RecursiveUrlLoader( url=urlCVE-2024-0243 · Other software · langchain-ai · reported by security@huntr.devHigh 8.1
With the following crawler configuration: ```python from bs4 import BeautifulSoup as Soup url = "https://example.com" loader = RecursiveUrlLoader( url=url, max_depth=2, extractor=lambda x: Soup(x, "html.parser").text ) docs = loader.load() ``` An attacker in control of the contents of `https://example.com` could place a malicious HTML file in there with links like "https://example.completely.different/my_file.html" and the crawler would proceed to download that file as well even though `prevent_outside=True`. https://github.com/langchain-ai/langchain/blob/bf0b3cc0b5ade1fb95a5b1b6fa260e99064c2e22/libs/community/langchain_community/document_loaders/recursive_url_loader.py#L51-L51 Resolved in https://github.com/langchain-ai/langchain/pull/15559
- Product
- langchain-ai/langchain
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`ChoCVE-2024-26152 · Other software · HumanSignal · reported by GitHubMedium 4.7
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 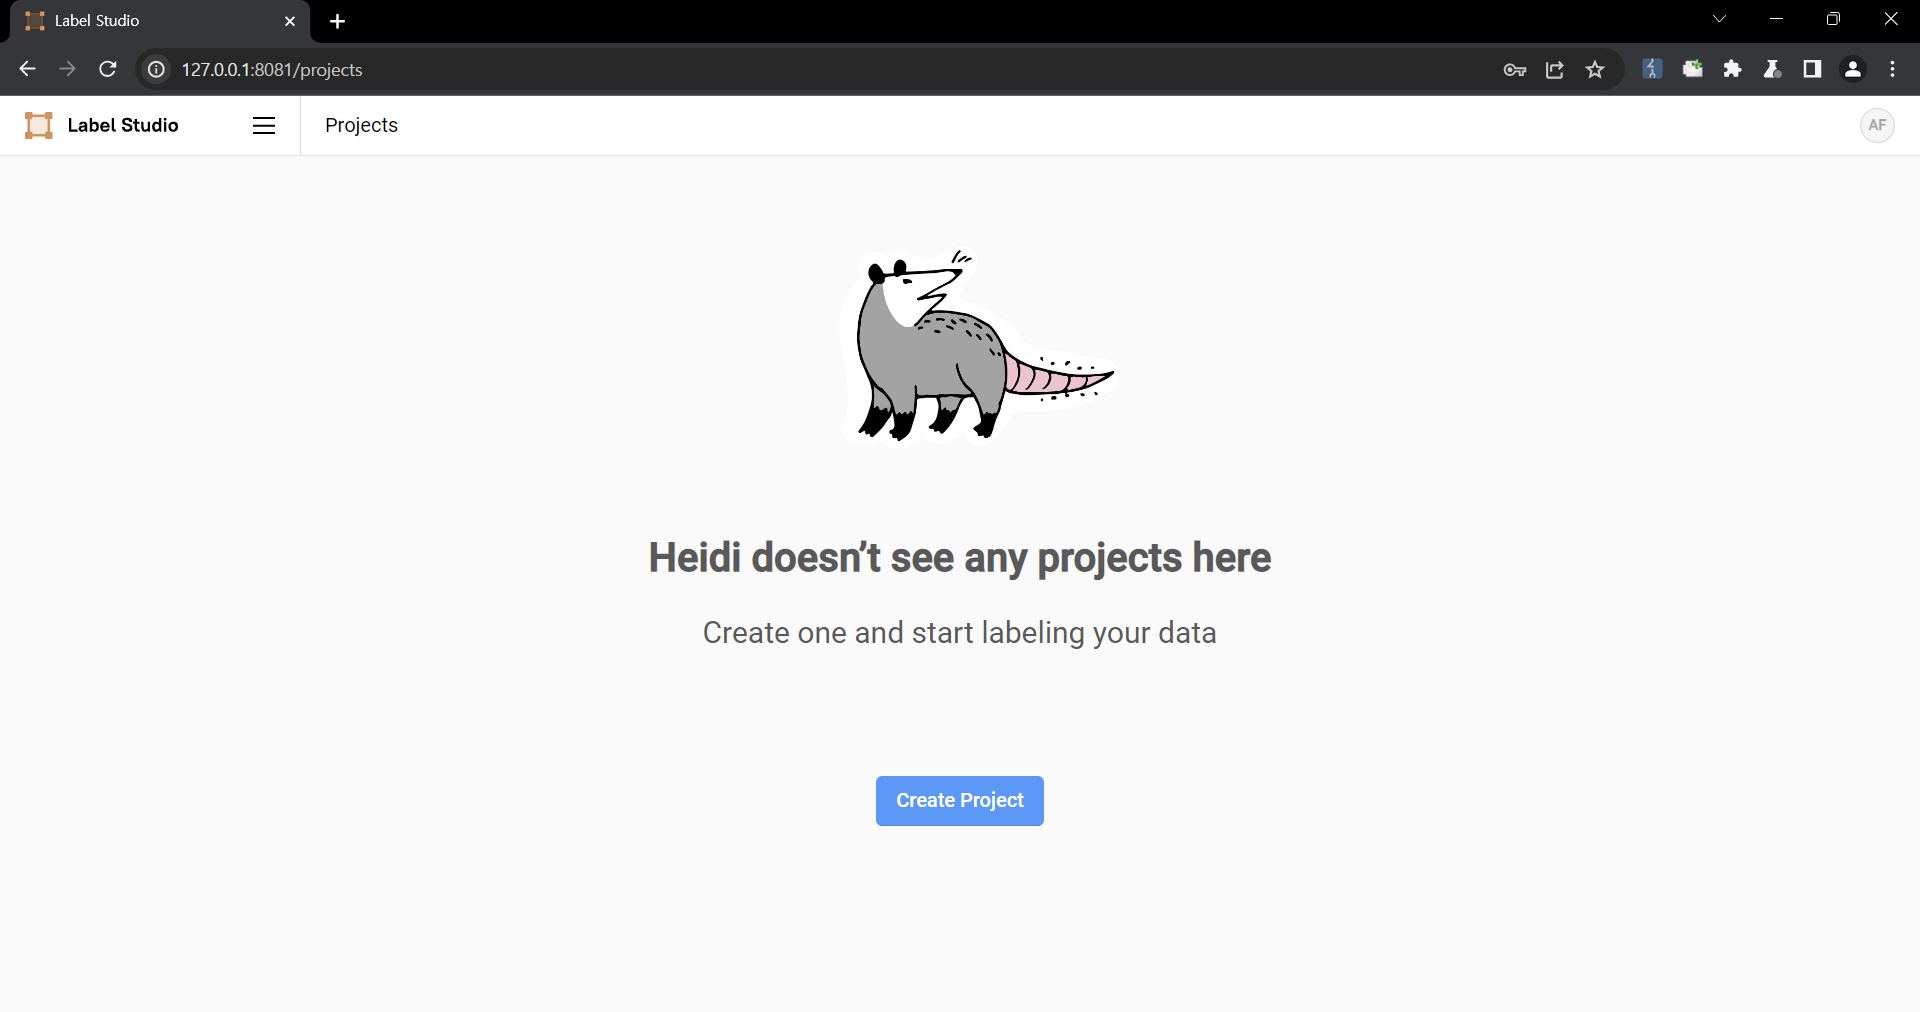 2. Upload a file containing the payload using the "Upload Files" function. 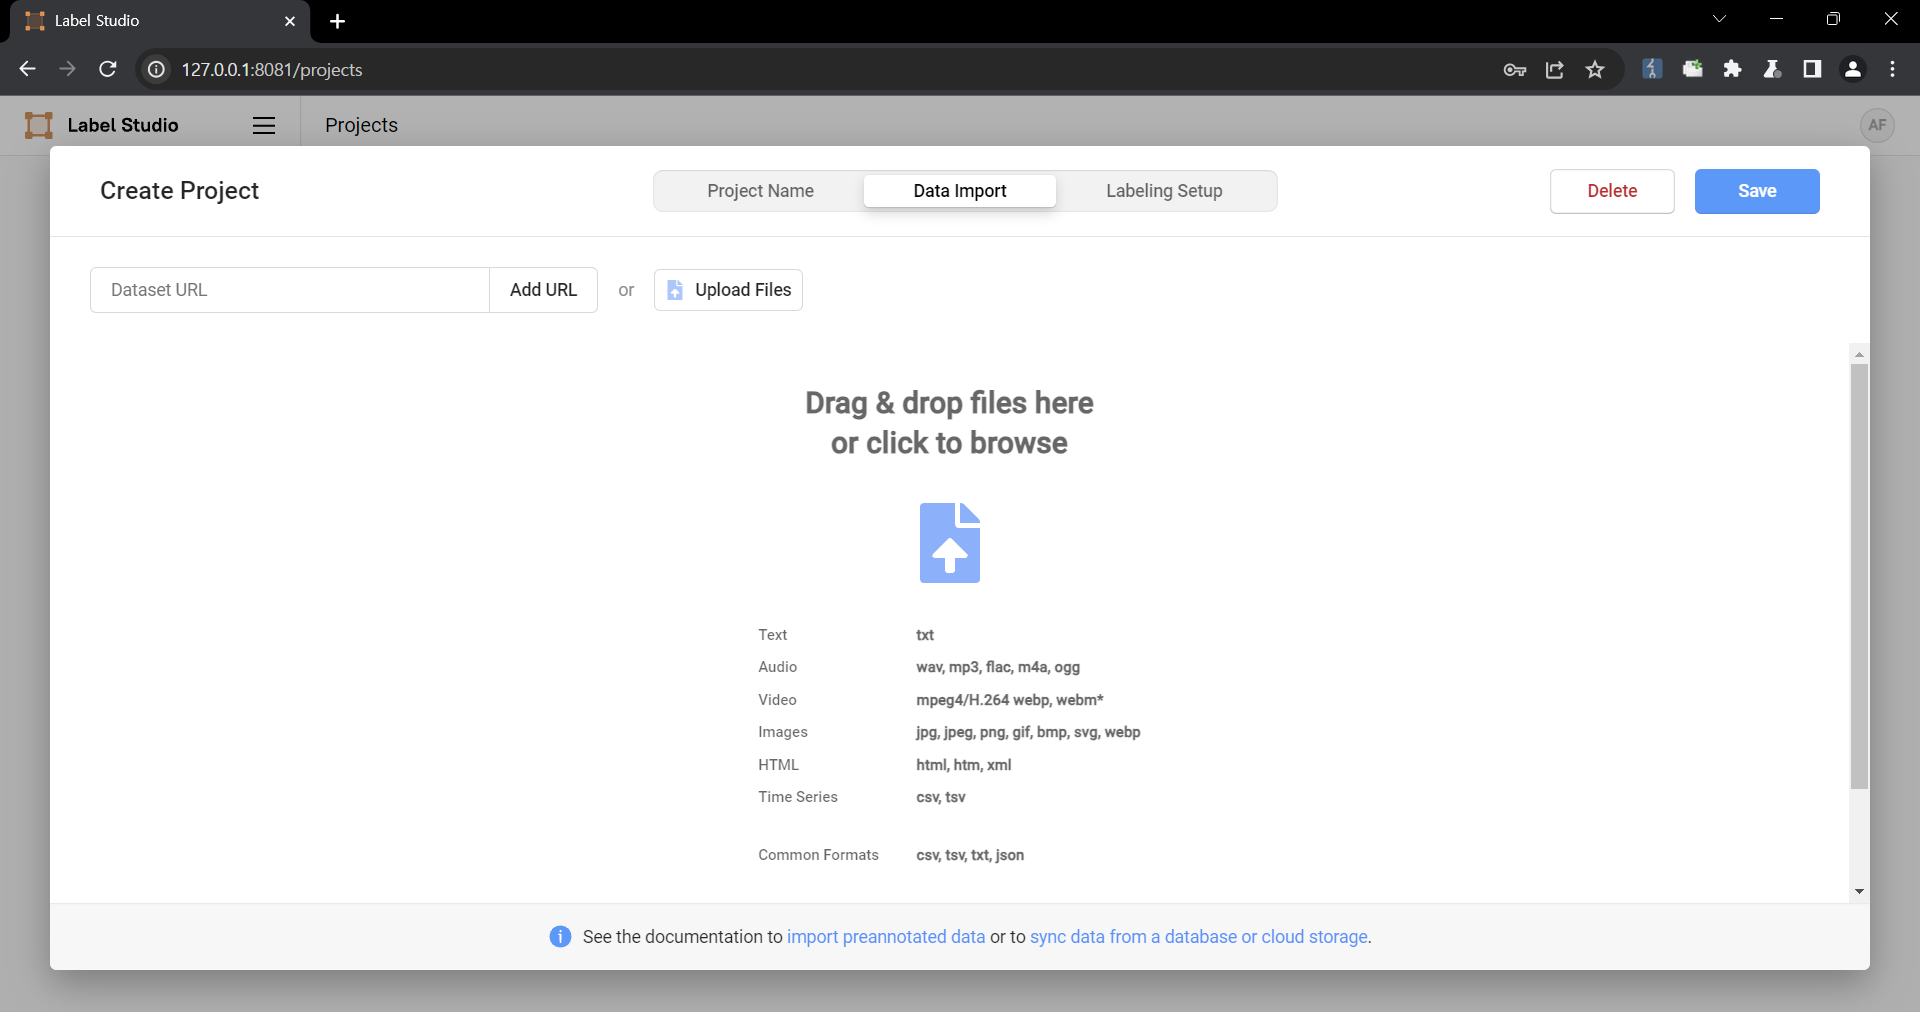 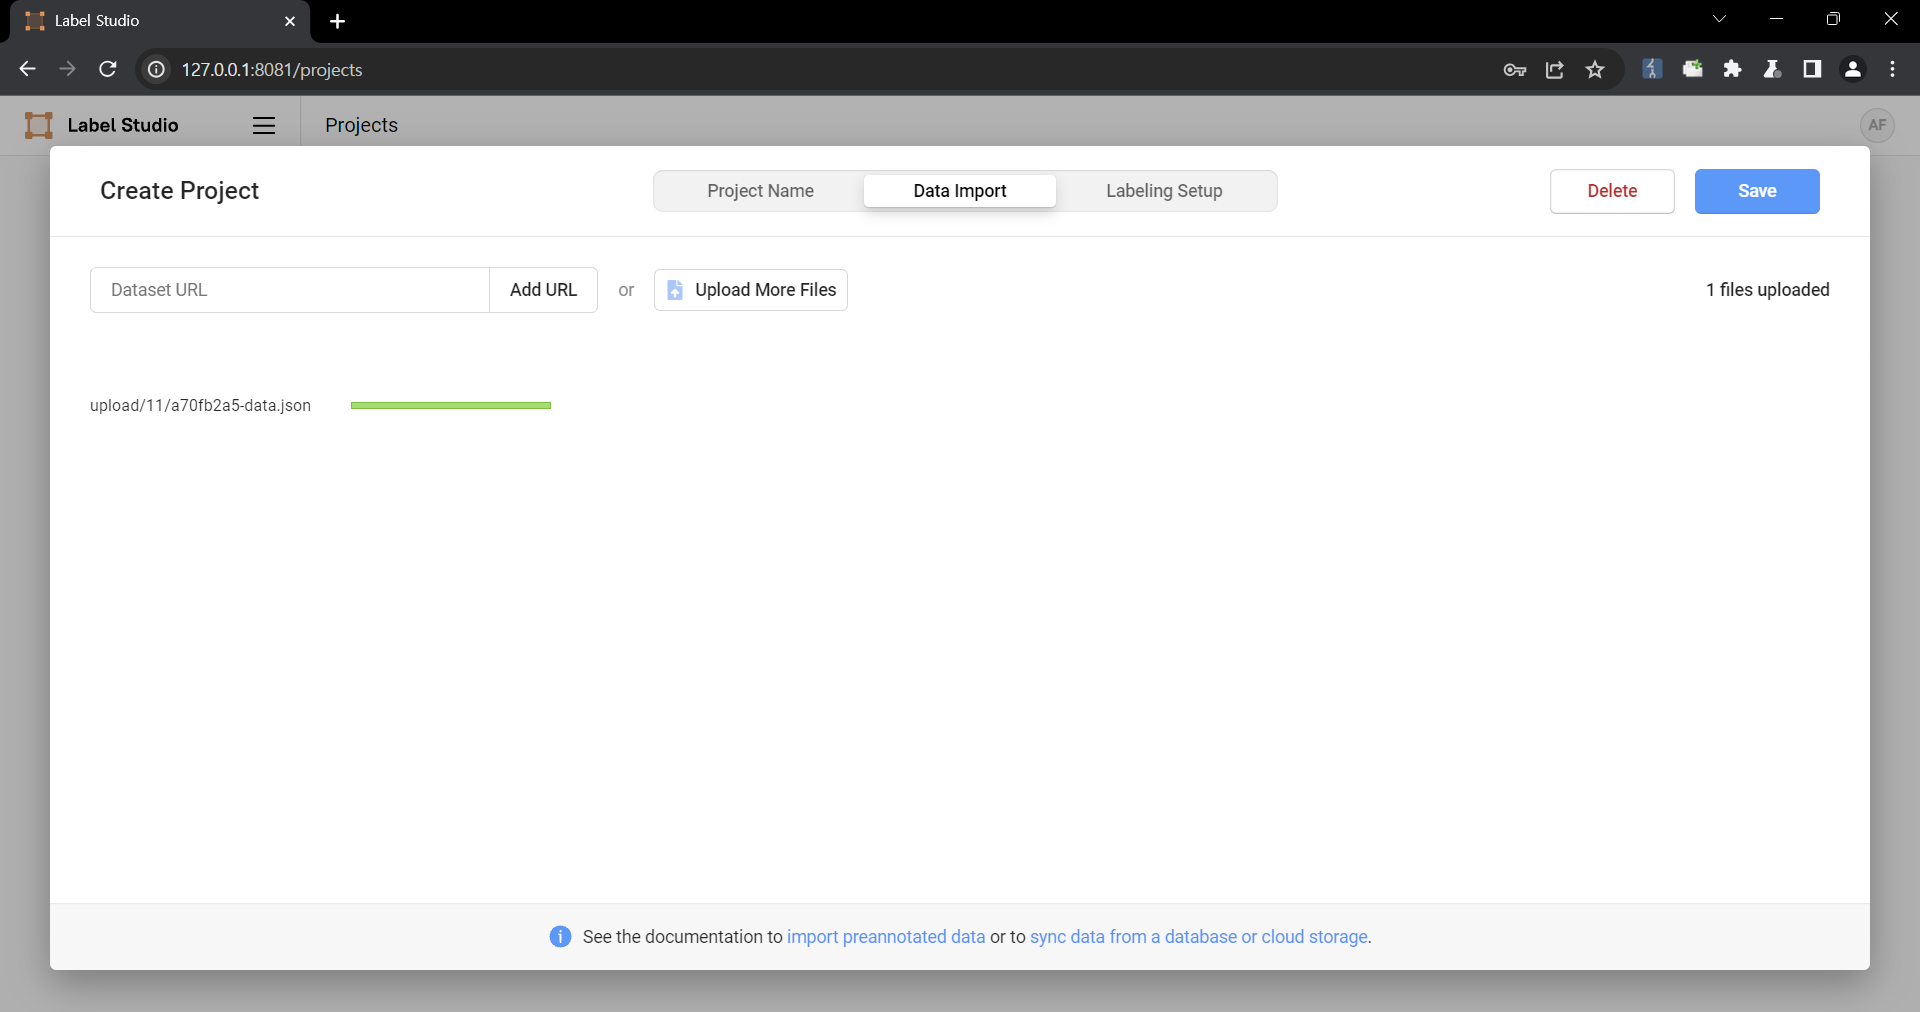 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 21, 2024A maliciously crafted STP file, when parsed in ASMIMPORT229A.dll, ASMKERN228A.dll, ASMkern229A.dll or ASMDATAX228A.dll through Autodesk applications, can lead tCVE-2024-23131 · Other software · Autodesk · reported by psirt@autodesk.comHigh 7.8
A maliciously crafted STP file, when parsed in ASMIMPORT229A.dll, ASMKERN228A.dll, ASMkern229A.dll or ASMDATAX228A.dll through Autodesk applications, can lead to a memory corruption vulnerability by write access violation. This vulnerability, in conjunction with other vulnerabilities, can lead to code execution in the context of the current process.
- Product
- AutoCAD
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordautodesk.comautodesk.com
Feb 21, 2024A maliciously crafted STP file, when parsed in ASMIMPORT228A.dll through Autodesk AutoCAD, may force an Out-of-Bounds Write vulnerability.CVE-2024-23124 · Other software · Autodesk · reported by psirt@autodesk.comHigh 7.8
A maliciously crafted STP file, when parsed in ASMIMPORT228A.dll through Autodesk AutoCAD, may force an Out-of-Bounds Write vulnerability. A malicious actor may leverage this vulnerability to cause a crash, cause data corruption, or execute arbitrary code in the context of the current process.
- Product
- AutoCAD
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordautodesk.comautodesk.com
Feb 21, 2024A maliciously crafted STP and STEP file, when parsed in ASMIMPORT228A.dll and ASMIMPORT229A.dll through Autodesk AutoCAD, may force an Out-of-Bounds Write vulneCVE-2024-23120 · Other software · Autodesk · reported by psirt@autodesk.comHigh 7.8
A maliciously crafted STP and STEP file, when parsed in ASMIMPORT228A.dll and ASMIMPORT229A.dll through Autodesk AutoCAD, may force an Out-of-Bounds Write vulnerability. A malicious actor may leverage this vulnerability to cause a crash, cause data corruption, or execute arbitrary code in the context of the current process.
- Product
- AutoCAD
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordautodesk.comautodesk.com
Feb 15, 2024A XSLT Server Side injection vulnerability in the Import Jobs function of FireBear Improved Import And Export v3.8.6 allows attackers to execute arbitrary commaCVE-2024-25413 · Other software · firebear_studio · reported by MITREHigh 7.2
A XSLT Server Side injection vulnerability in the Import Jobs function of FireBear Improved Import And Export v3.8.6 allows attackers to execute arbitrary commands via a crafted XSLT file.
- Product
- improved_import_and_export
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgithub.compacketstormsecurity.com
Feb 9, 2024Concrete CMS in version 9 before 9.2.5 is vulnerable to reflected XSS via the Image URL Import Feature due to insufficient validation of administrator provided CVE-2024-1246 · Other software · Concrete CMS · reported by ff5b8ace-8b95-4078-9743-eac1ca5451deLow 2
Concrete CMS in version 9 before 9.2.5 is vulnerable to reflected XSS via the Image URL Import Feature due to insufficient validation of administrator provided data. A rogue administrator could inject malicious code when importing images, leading to the execution of the malicious code on the website user’s browser. The Concrete CMS Security team scored this 2 with CVSS v3 vector AV:N/AC:H/PR:H/UI:R/S:U/C:L/I:N/A:N. This does not affect Concrete versions prior to version 9.
- Product
- Concrete CMS
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocumentation.concretecms.orgconcretecms.org
Feb 6, 2024The XML parser in Magic xpi Integration Platform 4.13.4 allows XXE attacks, e.g., via onItemImport.CVE-2023-52239 · Other software · Magicsoftware · reported by MITREMedium 6.5
The XML parser in Magic xpi Integration Platform 4.13.4 allows XXE attacks, e.g., via onItemImport.
- Product
- Magic XPI Integration Platform
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordds-security.comwww2.magicsoftware.com
Jan 24, 2024Product Import Export for WooCommerce: Unrestricted Upload of File with Dangerous TypeCVE-2024-22152 · WordPress plugins & themes · reported by PatchstackHigh 8
Unrestricted Upload of File with Dangerous Type vulnerability in WebToffee Product Import Export for WooCommerce.This issue affects Product Import Export for WooCommerce: from n/a through 2.3.7.
- Product
- Product Import Export for WooCommerce
- Affected
- up to 2.3.7
- What to do
- Affects up to 2.3.7. Update Product Import Export for WooCommerce to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Jan 24, 2024Order Export & Order Import for WooCommerce: Unrestricted Upload of File with Dangerous TypeCVE-2024-22135 · WordPress plugins & themes · reported by PatchstackHigh 8
Unrestricted Upload of File with Dangerous Type vulnerability in WebToffee Order Export & Order Import for WooCommerce.This issue affects Order Export & Order Import for WooCommerce: from n/a through 2.4.3.
- Product
- Order Export & Order Import for WooCommerce
- Affected
- up to 2.4.3
- What to do
- Affects up to 2.4.3. Update Order Export & Order Import for WooCommerce to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Jan 23, 2024Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and couldCVE-2024-23633 · Other software · HumanSignal · reported by GitHubMedium 4.7
Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and could be viewed on the website. Prior to version 1.10.1, this feature could had been abused to download a HTML file that executed malicious JavaScript code in the context of the Label Studio website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. `data_import/uploader.py` lines 125C5 through 146 showed that if a URL passed the server side request forgery verification checks, the contents of the file would be downloaded using the filename in the URL. The downloaded file path could then be retrieved by sending a request to `/api/projects/{project_id}/file-uploads?ids=[{download_id}]` where `{project_id}` was the ID of the project and `{download_id}` was the ID of the downloaded file. Once the downloaded file path was retrieved by the previous API endpoint, `data_import/api.py`lines
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddeveloper.mozilla.orggithub.com
Jan 22, 2024Import any XML or CSV File to: Accepts all zip files and automatically extracts the zip file into a publicly accessible directory without sufficiently validating the extracted file typeCVE-2023-7082 · WordPress plugins & themes · reported by WPScanHigh 7.2
The Import any XML or CSV File to WordPress plugin before 3.7.3 accepts all zip files and automatically extracts the zip file into a publicly accessible directory without sufficiently validating the extracted file type. This may allows high privilege users such as administrator to upload an executable file type leading to remote code execution.
- Product
- Import any XML or CSV File to
- Fixed in
- 3.7.3
- What to do
- Update Import any XML or CSV File to to 3.7.3 or newer.
Jan 16, 2024Theme Demo Import WordPress plugin before 1.1.1 does not validate the imported file, allowing high-privilege users such as admin to upload arbitrary files (suchCVE-2022-1538 · WordPress plugins & themes · reported by WPScanHigh 7.2
Theme Demo Import WordPress plugin before 1.1.1 does not validate the imported file, allowing high-privilege users such as admin to upload arbitrary files (such as PHP) even when FILE_MODS and FILE_EDIT are disallowed.
- Fixed in
- 1.1.1
- What to do
- Update the plugin to 1.1.1 or newer.
Jan 11, 2024Import and export users and customers: Stored Cross-Site ScriptingCVE-2023-6624 · WordPress plugins & themes · reported by WordfenceMedium 4.9
The Import and export users and customers plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin's shortcode(s) in all versions up to, and including, 1.24.3 due to insufficient input sanitization and output escaping on user supplied attributes. This makes it possible for authenticated attackers with contributor-level and above permissions to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Product
- Import and export users and customers
- Affected
- up to 1.24.3
- What to do
- Affects up to 1.24.3. Update Import and export users and customers to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgwordfence.com
Jan 11, 2024Import and export users and customers: Directory TraversalCVE-2023-6583 · WordPress plugins & themes · reported by WordfenceMedium 6.6
The Import and export users and customers plugin for WordPress is vulnerable to Directory Traversal in all versions up to, and including, 1.24.2 via the Recurring Import functionality. This makes it possible for authenticated attackers, with administrator access and above, to read and delete the contents of arbitrary files on the server including wp-config.php, which can contain sensitive information.
- Product
- Import and export users and customers
- Affected
- up to 1.24.2
- What to do
- Affects up to 1.24.2. Update Import and export users and customers to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgwordfence.com
Jan 11, 2024Export and Import Users and Customers: Arbitrary file uploadsCVE-2023-6558 · WordPress plugins & themes · reported by WordfenceHigh 7.2
The Export and Import Users and Customers plugin for WordPress is vulnerable to arbitrary file uploads due to insufficient file type validation on the 'upload_import_file' function in versions up to, and including, 2.4.8. This makes it possible for authenticated attackers with shop manager-level capabilities or above, to upload arbitrary files on the affected site's server which may make remote code execution possible.
- Product
- Export and Import Users and Customers
- Affected
- up to 2.4.8
- What to do
- Affects up to 2.4.8. Update Export and Import Users and Customers to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgplugins.trac.wordpress.org
Jan 10, 2024A unrestricted php file upload vulnerability exists in the import.json.php temporary copy functionality of WWBN AVideo dev master commit 15fed957fb.CVE-2023-49715 · Other software · WWBN · reported by talos-cna@cisco.comMedium 4.3
A unrestricted php file upload vulnerability exists in the import.json.php temporary copy functionality of WWBN AVideo dev master commit 15fed957fb. A specially crafted HTTP request can lead to arbitrary code execution when chained with an LFI vulnerability. An attacker can send a series of HTTP requests to trigger this vulnerability.
- Product
- AVideo
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordtalosintelligence.comtalosintelligence.com
Dec 26, 2023JSON Content Importer: Does not sanitise and escape the tab parameter before outputting it back in the pageCVE-2023-6268 · WordPress plugins & themes · reported by WPScanMedium 6.1
The JSON Content Importer WordPress plugin before 1.5.4 does not sanitise and escape the tab parameter before outputting it back in the page, leading to a Reflected Cross-Site Scripting which could be used against high privilege users such as admin
- Product
- JSON Content Importer
- Fixed in
- 1.5.4
- What to do
- Update JSON Content Importer to 1.5.4 or newer.
Dec 26, 2023rtMedia for WordPress, BuddyPress and bbPress: Loads the contents of the import file in an unsafe mannerCVE-2023-5939 · WordPress plugins & themes · reported by WPScanHigh 7.2
The rtMedia for WordPress, BuddyPress and bbPress WordPress plugin before 4.6.16 loads the contents of the import file in an unsafe manner, leading to remote code execution by privileged users.
- Product
- rtMedia for WordPress, BuddyPress and bbPress
- Fixed in
- 4.6.16
- What to do
- Update rtMedia for WordPress, BuddyPress and bbPress to 4.6.16 or newer.
Dec 23, 2023Widget Settings Importer/Exporter: Stored Cross-Site ScriptingCVE-2020-36769 · WordPress plugins & themes · reported by WordfenceHigh 7.4
The Widget Settings Importer/Exporter Plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the wp_ajax_import_widget_dataparameter AJAX action in versions up to, and including, 1.5.3 due to insufficient input sanitization and output escaping. This makes it possible for authenticated attackers with subscriber-level permissions and above to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Product
- Widget Settings Importer/Exporter
- Affected
- up to 1.5.3
- What to do
- Affects up to 1.5.3. Update Widget Settings Importer/Exporter to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordwordfence.comwordfence.com
Dec 20, 2023Export Import Menus: Unrestricted Upload of File with Dangerous TypeCVE-2023-34385 · WordPress plugins & themes · reported by PatchstackCritical 9.9
Unrestricted Upload of File with Dangerous Type vulnerability in Akshay Menariya Export Import Menus.This issue affects Export Import Menus: from n/a through 1.8.0.
- Product
- Export Import Menus
- Affected
- up to 1.8.0
- What to do
- Affects up to 1.8.0. Update Export Import Menus to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Dec 20, 2023Olive One Click Demo Import: Unrestricted Upload of File with Dangerous TypeCVE-2023-29102 · WordPress plugins & themes · reported by PatchstackCritical 9.1
Unrestricted Upload of File with Dangerous Type vulnerability in Olive Themes Olive One Click Demo Import.This issue affects Olive One Click Demo Import: from n/a through 1.1.1.
- Product
- Olive One Click Demo Import
- Affected
- up to 1.1.1
- What to do
- Affects up to 1.1.1. Update Olive One Click Demo Import to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Dec 20, 2023Theme Demo Import: Unrestricted Upload of File with Dangerous TypeCVE-2023-28170 · WordPress plugins & themes · reported by PatchstackCritical 9.1
Unrestricted Upload of File with Dangerous Type vulnerability in Themely Theme Demo Import.This issue affects Theme Demo Import: from n/a through 1.1.1.
- Product
- Theme Demo Import
- Affected
- up to 1.1.1
- What to do
- Affects up to 1.1.1. Update Theme Demo Import to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Dec 19, 2023Uncontrolled resource consumption can be triggered by authenticated attacker that uploads a malicious ZIP to import database, dashboards or datasets.CVE-2023-46104 · Websites & servers · Apache Software Foundation · reported by security@apache.orgMedium 6.5
Uncontrolled resource consumption can be triggered by authenticated attacker that uploads a malicious ZIP to import database, dashboards or datasets. This vulnerability exists in Apache Superset versions up to and including 2.1.2 and versions 3.0.0, 3.0.1.
- Product
- Apache Superset
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordopenwall.comopenwall.com
Dec 17, 2023CSV Importer: Cross-Site Request Forgery (CSRF)CVE-2023-49775 · WordPress plugins & themes · reported by PatchstackMedium 4.3
Cross-Site Request Forgery (CSRF) vulnerability in Denis Kobozev CSV Importer.This issue affects CSV Importer: from n/a through 0.3.8.
- Product
- CSV Importer
- Affected
- up to 0.3.8
- What to do
- Affects up to 0.3.8. Update CSV Importer to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Nov 30, 2023Import Spreadsheets from Microsoft Excel: Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting')CVE-2023-48289 · WordPress plugins & themes · reported by PatchstackMedium 6.5
Improper Neutralization of Input During Web Page Generation ('Cross-site Scripting') vulnerability in SpreadsheetConverter Import Spreadsheets from Microsoft Excel allows Stored XSS.This issue affects Import Spreadsheets from Microsoft Excel: from n/a through 10.1.3.
- Product
- Import Spreadsheets from Microsoft Excel
- Affected
- up to 10.1.3
- What to do
- Affects up to 10.1.3. Update Import Spreadsheets from Microsoft Excel to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordpatchstack.compatchstack.com
Nov 27, 2023Mattermost fails to limit the amount of data extracted from compressed archives during board import in Mattermost Boards allowing an attacker to consume excessiCVE-2023-48268 · Other software · Mattermost · reported by responsibledisclosure@mattermost.comMedium 4.3
Mattermost fails to limit the amount of data extracted from compressed archives during board import in Mattermost Boards allowing an attacker to consume excessive resources, possibly leading to Denial of Service, by importing a board using a specially crafted zip (zip bomb).
- Product
- Mattermost
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmattermost.commattermost.com
Where this comes from: the exploited list is CISA’s Known Exploited Vulnerabilities catalog. Everything else is the whole National Vulnerability Database, where each record is published by the team that found the bug (Wordfence, Patchstack, WPScan, the vendors themselves and others); we show who. Exploit odds are FIRST’s EPSS, updated daily. Titles and categories are ours, so check the linked record before acting on a detail. For a write-up of the big ones, see our advisories. Every vendor, and every WordPress plugin and theme with a recorded flaw, also has its own page. All of it is free to reuse as JSON, CSV or RSS.
Weekly security brief
The flaws that hit local websites, every Friday.
One short email: what got exploited this week, which WordPress plugins broke, and what to check. Unsubscribe in one click.
Tell us what you're building.
A website, your marketing, a security check, an app, or the thing you've been running out of a spreadsheet for three years. A few lines is plenty.
Not ready to talk yet? Run the free website check and see what Google sees.