Vulnerability database
Every flaw the U.S. government’s cybersecurity agency (CISA) has confirmed attackers are using, plus the new WordPress plugin and theme bugs published each day, sorted by what they mean for a small business. We refresh it twice a day. If you see something your website or office runs, tell us.
1,269 results · page 10 of 26
May 14, 2024Improper DLL loading algorithms in B&R Automation Studio versions >=4.0 and <4.12 may allow an authenticated local attacker to execute code in the context of thCVE-2021-22280 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 7.2
Improper DLL loading algorithms in B&R Automation Studio versions >=4.0 and <4.12 may allow an authenticated local attacker to execute code in the context of the product.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
May 14, 2024Visual Studio Denial of Service VulnerabilityCVE-2024-30046 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comMedium 5.9
Visual Studio Denial of Service Vulnerability
- Product
- .NET 7.0
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
May 14, 2024.NET and Visual Studio Remote Code Execution VulnerabilityCVE-2024-30045 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comMedium 6.3
.NET and Visual Studio Remote Code Execution Vulnerability
- Product
- .NET 8.0
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
May 14, 2024A deserialization of untrusted data vulnerability exists in common code used by FlexLogger and InstrumentStudio that may result in remote code execution.CVE-2024-4044 · Other software · NI · reported by security@ni.comHigh 7.8
A deserialization of untrusted data vulnerability exists in common code used by FlexLogger and InstrumentStudio that may result in remote code execution. Successful exploitation requires an attacker to get a user to open a specially crafted project file. This vulnerability affects NI FlexLogger 2024 Q1 and prior versions as well as NI InstrumentStudio 2024 Q1 and prior versions.
- Product
- FlexLogger
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
May 2, 2024LA-Studio Element Kit for Elementor: Stored Cross-Site ScriptingCVE-2024-3005 · WordPress plugins & themes · reported by WordfenceMedium 6.4
The LA-Studio Element Kit for Elementor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the plugin's LaStudioKit Post Author widget in all versions up to, and including, 1.3.7.5 due to insufficient input sanitization and output escaping on user supplied attributes. This makes it possible for authenticated attackers, with contributor-level access and above, to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Product
- LA-Studio Element Kit for Elementor
- Affected
- up to 1.3.7.5
- What to do
- Affects up to 1.3.7.5. Update LA-Studio Element Kit for Elementor to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgwordfence.com
Apr 29, 2024Cross Site Scripting (XSS) in Beekeeper Studio 4.1.13 and earlier allows remote attackers to execute arbitrary code in the column name of a database table in taCVE-2024-23995 · Other software · beekeeperstudio · reported by MITREMedium 6.1
Cross Site Scripting (XSS) in Beekeeper Studio 4.1.13 and earlier allows remote attackers to execute arbitrary code in the column name of a database table in tabulator-popup-container.
- Product
- beekeeper-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgithub.combeekeeperstudio.io
Apr 28, 2024IBM i 7.2, 7.3, 7.4, 7.5 and IBM Rational Development Studio for i 7.2, 7.3, 7.4, 7.5 networking and compiler infrastructure could allow a local user to gain elCVE-2024-25050 · Other software · IBM · reported by psirt@us.ibm.comHigh 8.4
IBM i 7.2, 7.3, 7.4, 7.5 and IBM Rational Development Studio for i 7.2, 7.3, 7.4, 7.5 networking and compiler infrastructure could allow a local user to gain elevated privileges due to an unqualified library call. A malicious actor could cause user-controlled code to run with administrator privileges. IBM X-Force ID: 283242.
- Product
- i
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordexchange.xforce.ibmcloud.comibm.com
Apr 15, 2024Out-of-bounds read vulnerability exists in KV STUDIO Ver.11.64 and earlier and KV REPLAY VIEWER Ver.2.64 and earlier, and VT5-WX15/WX12 Ver.6.02 and earlier, whCVE-2024-29219 · Other software · KEYENCE CORPORATION · reported by vultures@jpcert.or.jpHigh 7.8
Out-of-bounds read vulnerability exists in KV STUDIO Ver.11.64 and earlier and KV REPLAY VIEWER Ver.2.64 and earlier, and VT5-WX15/WX12 Ver.6.02 and earlier, which may lead to information disclosure or arbitrary code execution by having a user of the affected product open a specially crafted file.
- Product
- KV STUDIO
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Apr 15, 2024Out-of-bounds write vulnerability exists in KV STUDIO Ver.11.64 and earlier, KV REPLAY VIEWER Ver.2.64 and earlier, and VT5-WX15/WX12 Ver.6.02 and earlier, whicCVE-2024-29218 · Other software · KEYENCE CORPORATION · reported by vultures@jpcert.or.jpHigh 8.8
Out-of-bounds write vulnerability exists in KV STUDIO Ver.11.64 and earlier, KV REPLAY VIEWER Ver.2.64 and earlier, and VT5-WX15/WX12 Ver.6.02 and earlier, which may lead to information disclosure or arbitrary code execution by having a user of the affected product open a specially crafted file.
- Product
- KV STUDIO
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Apr 15, 2024VT STUDIO Ver.8.32 and earlier contains an issue with the DLL search path, which may lead to insecurely loading Dynamic Link Libraries.CVE-2024-28099 · Other software · KEYENCE CORPORATION · reported by vultures@jpcert.or.jpHigh 7.8
VT STUDIO Ver.8.32 and earlier contains an issue with the DLL search path, which may lead to insecurely loading Dynamic Link Libraries. As a result, arbitrary code may be executed with the privileges of the running application.
- Product
- VT STUDIO
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Apr 9, 2024Microsoft ODBC Driver for SQL Server Remote Code Execution VulnerabilityCVE-2024-28933 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 8.8
Microsoft ODBC Driver for SQL Server Remote Code Execution Vulnerability
- Product
- Microsoft Visual Studio 2019 version 16.11 (includes 16.0 - 16.10)
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Apr 9, 2024.NET, .NET Framework, and Visual Studio Remote Code Execution VulnerabilityCVE-2024-21409 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.3
.NET, .NET Framework, and Visual Studio Remote Code Execution Vulnerability
- Product
- Microsoft Visual Studio 2022 version 17.9
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Mar 14, 2024LA-Studio Element Kit for Elementor: Stored Cross-Site ScriptingCVE-2024-2249 · WordPress plugins & themes · reported by WordfenceMedium 6.4
The LA-Studio Element Kit for Elementor plugin for WordPress is vulnerable to Stored Cross-Site Scripting via the LinkWrapper attribute found in several widgets in all versions up to, and including, 1.3.7.4 due to insufficient input sanitization and output escaping the user supplied attribute. This makes it possible for authenticated attackers with contributor-level and above permissions to inject arbitrary web scripts in pages that will execute whenever a user accesses an injected page.
- Product
- LA-Studio Element Kit for Elementor
- Affected
- up to 1.3.7.4
- What to do
- Affects up to 1.3.7.4. Update LA-Studio Element Kit for Elementor to the newest version and check its changelog mentions this fix; if there isn’t one yet, deactivate it until there is.
Full record and what to do →NVD recordplugins.trac.wordpress.orgwordfence.com
Mar 12, 2024Azure Data Studio Elevation of Privilege VulnerabilityCVE-2024-26203 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.3
Azure Data Studio Elevation of Privilege Vulnerability
- Product
- Azure Data Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Mar 12, 2024Microsoft QUIC Denial of Service VulnerabilityCVE-2024-26190 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.5
Microsoft QUIC Denial of Service Vulnerability
- Product
- Microsoft Visual Studio 2022 version 17.9
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Mar 12, 2024Visual Studio Code Elevation of Privilege VulnerabilityCVE-2024-26165 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 8.8
Visual Studio Code Elevation of Privilege Vulnerability
- Product
- Visual Studio Code
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Mar 12, 2024.NET and Visual Studio Denial of Service VulnerabilityCVE-2024-21392 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.5
.NET and Visual Studio Denial of Service Vulnerability
- Product
- Microsoft Visual Studio 2022 version 17.9
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Feb 22, 2024### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`ChoCVE-2024-26152 · Other software · HumanSignal · reported by GitHubMedium 4.7
### Summary On all Label Studio versions prior to 1.11.0, data imported via file upload feature is not properly sanitized prior to being rendered within a [`Choices`](https://labelstud.io/tags/choices) or [`Labels`](https://labelstud.io/tags/labels) tag, resulting in an XSS vulnerability. ### Details Need permission to use the "data import" function. This was reproduced on Label Studio 1.10.1. ### PoC 1. Create a project. 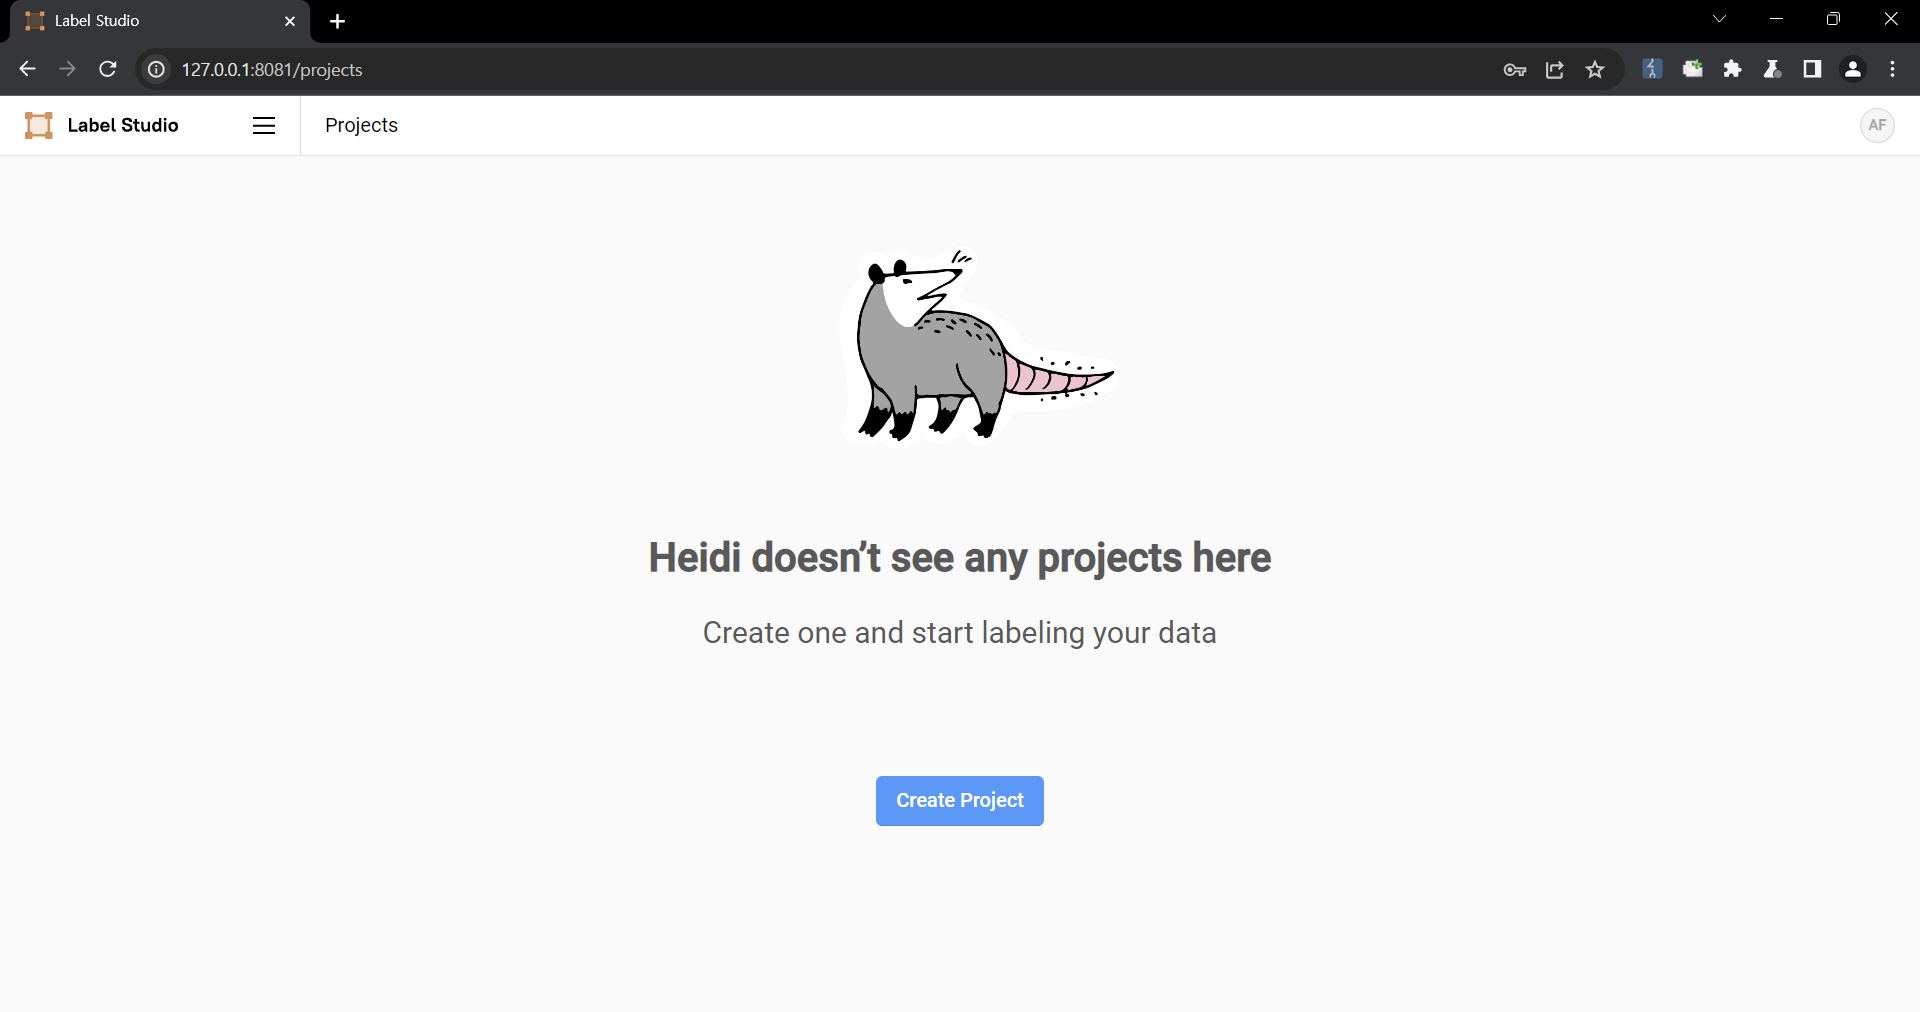 2. Upload a file containing the payload using the "Upload Files" function. 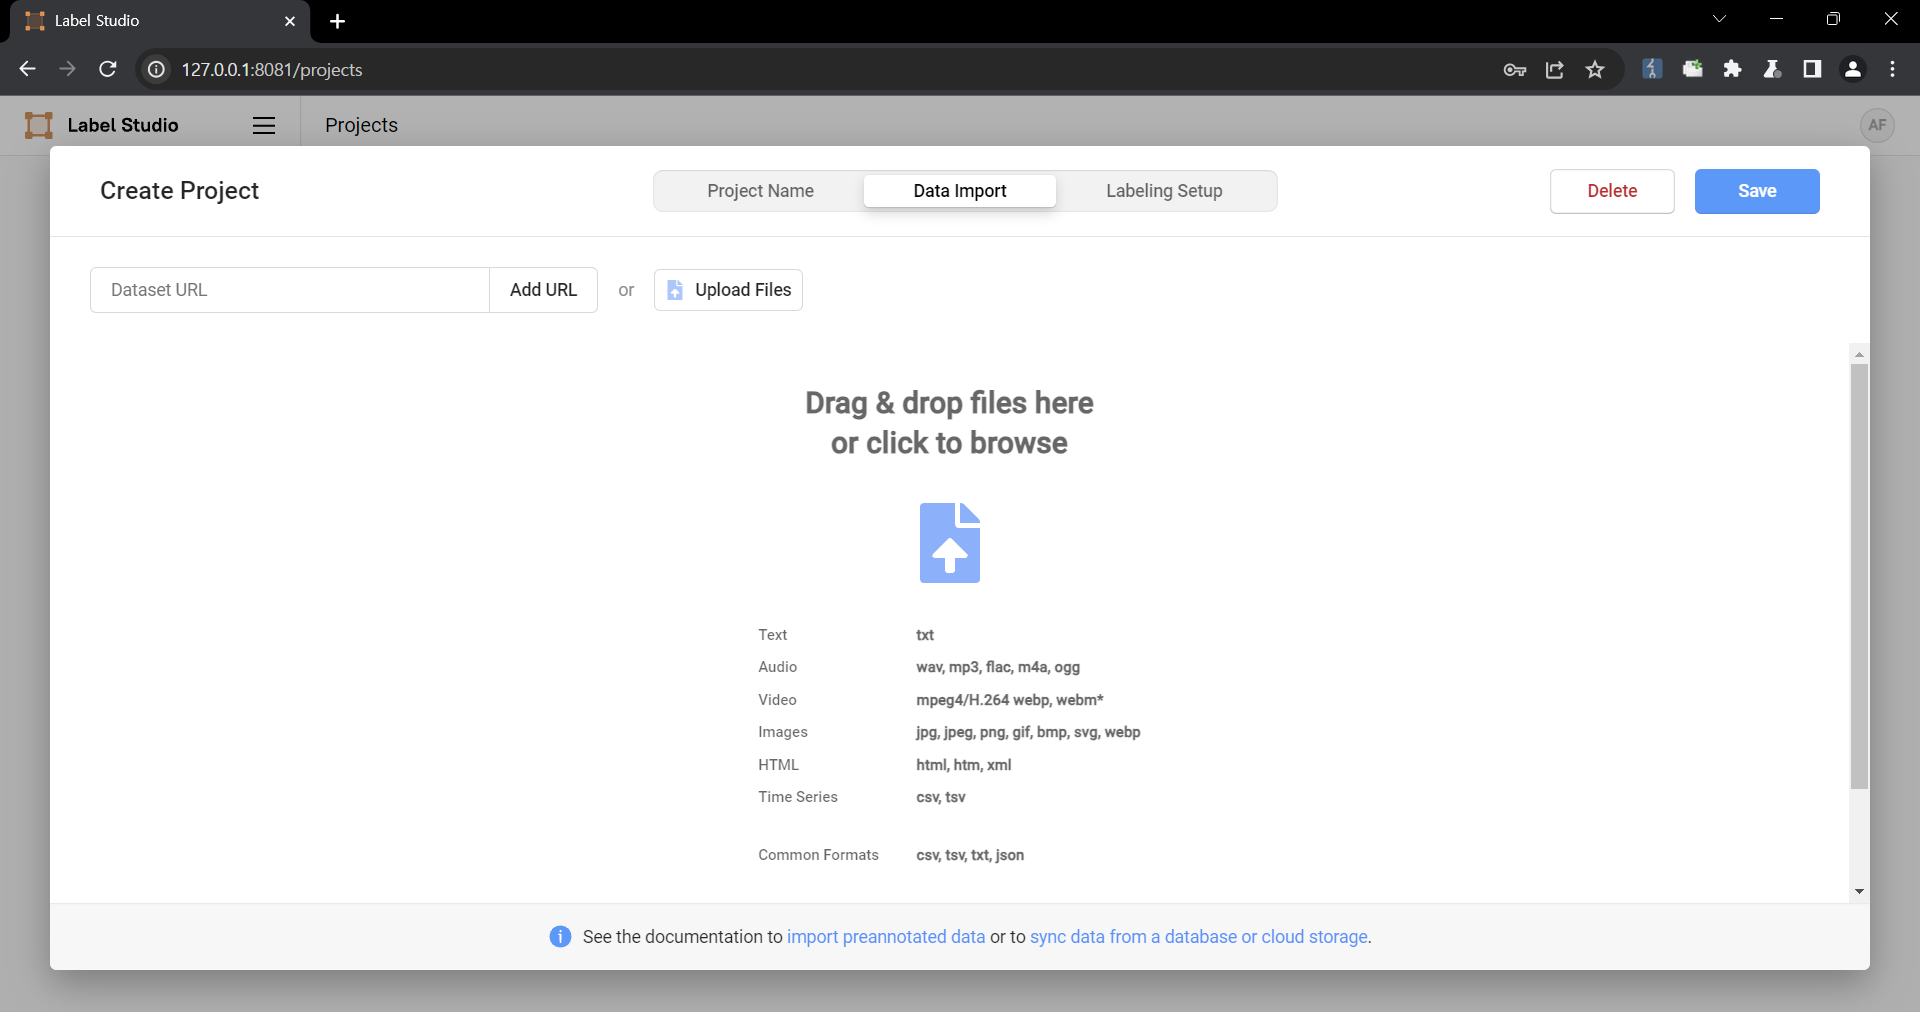 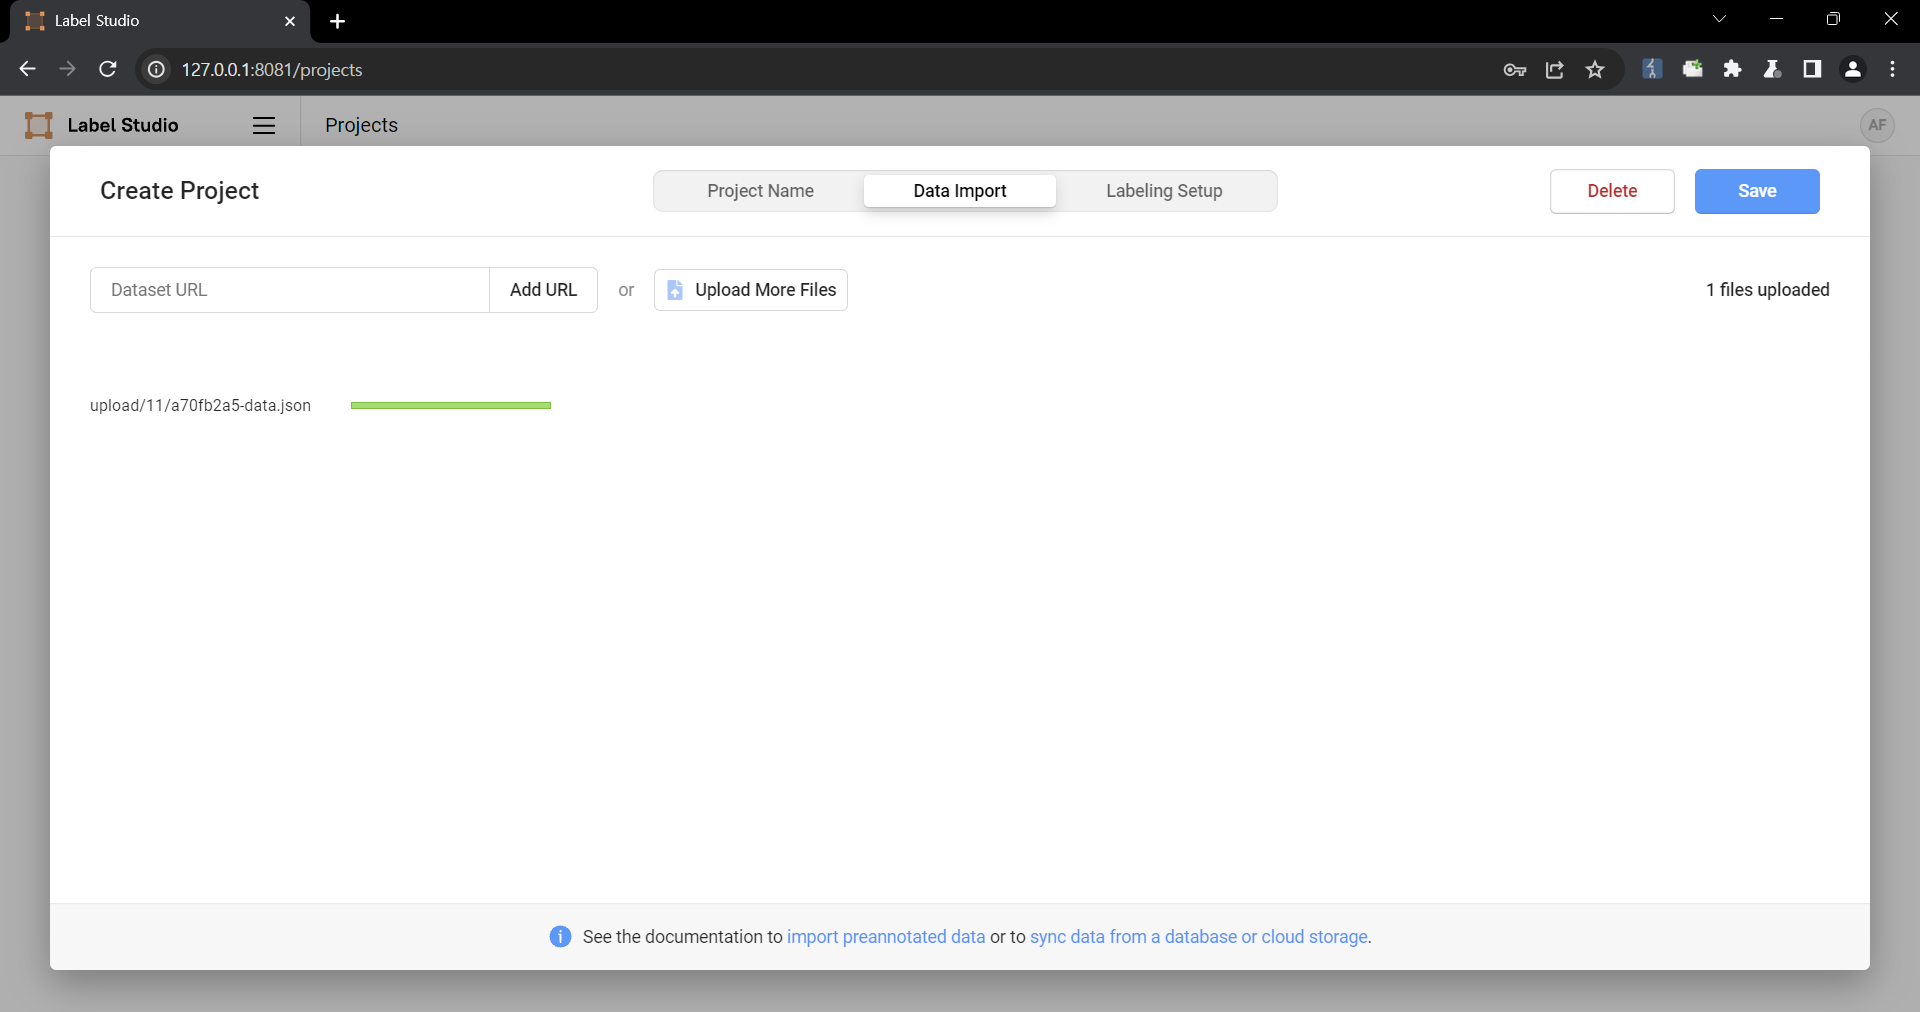 The following are the contents of the files used in the PoC ``` { "data": { "prompt": "labelstudio universe image", "images": [ { "value": "id123#0", "style": "margin: 5px", "html": "<img width='400' src='https://labelstud.io/_astro/images-tab.64279c16_
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024A reflected Cross-Site Scripting (XSS) vulnerability in FUEL CMS 1.5.2allows attackers to run arbitrary code via crafted string after the group_id parameter.CVE-2024-25369 · Other software · Thedaylightstudio · reported by MITREMedium 5.4
A reflected Cross-Site Scripting (XSS) vulnerability in FUEL CMS 1.5.2allows attackers to run arbitrary code via crafted string after the group_id parameter.
- Product
- Fuel CMS
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Feb 22, 2024B&R Automation Studio Upgrade Service and B&R Technology Guarding use insufficient cryptography for communication to the upgrade and the licensing servers.CVE-2024-0220 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 8.3
B&R Automation Studio Upgrade Service and B&R Technology Guarding use insufficient cryptography for communication to the upgrade and the licensing servers. A network-based attacker could exploit the vulnerability to execute arbitrary code on the products or sniff sensitive data.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 15, 2024A XSLT Server Side injection vulnerability in the Import Jobs function of FireBear Improved Import And Export v3.8.6 allows attackers to execute arbitrary commaCVE-2024-25413 · Other software · firebear_studio · reported by MITREHigh 7.2
A XSLT Server Side injection vulnerability in the Import Jobs function of FireBear Improved Import And Export v3.8.6 allows attackers to execute arbitrary commands via a crafted XSLT file.
- Product
- improved_import_and_export
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgithub.compacketstormsecurity.com
Feb 2, 2024: Relative Path Traversal vulnerability in B&R Industrial Automation Automation Studio allows Relative Path Traversal.This issue affects Automation Studio: fromCVE-2021-22281 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comMedium 6.3
: Relative Path Traversal vulnerability in B&R Industrial Automation Automation Studio allows Relative Path Traversal.This issue affects Automation Studio: from 4.0 through 4.12.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 2, 2024Unquoted Search Path or Element vulnerability in B&R Industrial Automation Automation Studio, B&R Industrial Automation NET/PVI allows Target Programs with ElevCVE-2020-24682 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 7.2
Unquoted Search Path or Element vulnerability in B&R Industrial Automation Automation Studio, B&R Industrial Automation NET/PVI allows Target Programs with Elevated Privileges.This issue affects Automation Studio: from 4.0 through 4.6, from 4.7.0 before 4.7.7 SP, from 4.8.0 before 4.8.6 SP, from 4.9.0 before 4.9.4 SP; NET/PVI: from 4.0 through 4.6, from 4.7.0 before 4.7.7, from 4.8.0 before 4.8.6, from 4.9.0 before 4.9.4.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 2, 2024Improper Control of Generation of Code ('Code Injection') vulnerability in B&R Industrial Automation Automation Studio allows Local Execution of Code.This issueCVE-2021-22282 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 8.3
Improper Control of Generation of Code ('Code Injection') vulnerability in B&R Industrial Automation Automation Studio allows Local Execution of Code.This issue affects Automation Studio: from 4.0 through 4.12.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 2, 2024Incorrect Permission Assignment for Critical Resource vulnerability in B&R Industrial Automation Automation Studio allows Privilege Escalation.This issue affectCVE-2020-24681 · Other software · B&R Industrial Automation · reported by cybersecurity@ch.abb.comHigh 8.2
Incorrect Permission Assignment for Critical Resource vulnerability in B&R Industrial Automation Automation Studio allows Privilege Escalation.This issue affects Automation Studio: from 4.6.0 through 4.6.X, from 4.7.0 before 4.7.7 SP, from 4.8.0 before 4.8.6 SP, from 4.9.0 before 4.9.4 SP.
- Product
- Automation Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordbr-automation.combr-automation.com
Feb 1, 2024 When SEW-EURODRIVE MOVITOOLS MotionStudio processes XML information unrestricted file access can occur.CVE-2024-1167 · Other software · SEW-EURODRIVE · reported by ics-cert@hq.dhs.govMedium 5.5
When SEW-EURODRIVE MOVITOOLS MotionStudio processes XML information unrestricted file access can occur.
- Product
- MOVITOOLS MotionStudio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordcisa.govseweurodrive.com
Feb 1, 2024An OS Command Injection vulnerability exists in BIOVIA Materials Studio products from Release BIOVIA 2021 through Release BIOVIA 2023.CVE-2023-6078 · Other software · Dassault Systèmes · reported by 3DS.Information-Security@3ds.comHigh 8.8
An OS Command Injection vulnerability exists in BIOVIA Materials Studio products from Release BIOVIA 2021 through Release BIOVIA 2023. Upload of a specially crafted perl script can lead to arbitrary command execution.
- Product
- BIOVIA Materials Studio products
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 31, 2024Label Studio is a popular open source data labeling tool.CVE-2023-47116 · Other software · HumanSignal · reported by GitHubMedium 5.3
Label Studio is a popular open source data labeling tool. The vulnerability affects all versions of Label Studio prior to 1.11.0 and was tested on version 1.8.2. Label Studio's SSRF protections that can be enabled by setting the `SSRF_PROTECTION_ENABLED` environment variable can be bypassed to access internal web servers. This is because the current SSRF validation is done by executing a single DNS lookup to verify that the IP address is not in an excluded subnet range. This protection can be bypassed by either using HTTP redirection or performing a DNS rebinding attack.
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 31, 2024In Telerik Test Studio versions prior to v2023.3.1330, a privilege elevation vulnerability has been identified in the applications installer component.CVE-2024-0833 · Other software · Progress Software · reported by security@progress.comHigh 7.8
In Telerik Test Studio versions prior to v2023.3.1330, a privilege elevation vulnerability has been identified in the applications installer component. In an environment where an existing Telerik Test Studio install is present, a lower privileged user has the ability to manipulate the installation package to elevate their privileges on the underlying operating system.
- Product
- Telerik Test Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocs.telerik.comtelerik.com
Jan 26, 2024An issue in kosei entertainment esportsstudioLegends mini-app on Line v13.6.1 allows attackers to send crafted malicious notifications via leakage of the channeCVE-2023-48132 · Other software · Linecorp · reported by MITREMedium 5.4
An issue in kosei entertainment esportsstudioLegends mini-app on Line v13.6.1 allows attackers to send crafted malicious notifications via leakage of the channel access token.
- Product
- Line
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 23, 2024Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and couldCVE-2024-23633 · Other software · HumanSignal · reported by GitHubMedium 4.7
Label Studio, an open source data labeling tool had a remote import feature allowed users to import data from a remote web source, that was downloaded and could be viewed on the website. Prior to version 1.10.1, this feature could had been abused to download a HTML file that executed malicious JavaScript code in the context of the Label Studio website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. `data_import/uploader.py` lines 125C5 through 146 showed that if a URL passed the server side request forgery verification checks, the contents of the file would be downloaded using the filename in the URL. The downloaded file path could then be retrieved by sending a request to `/api/projects/{project_id}/file-uploads?ids=[{download_id}]` where `{project_id}` was the ID of the project and `{download_id}` was the ID of the downloaded file. Once the downloaded file path was retrieved by the previous API endpoint, `data_import/api.py`lines
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddeveloper.mozilla.orggithub.com
Jan 23, 2024Label Studio is an a popular open source data labeling tool.CVE-2023-47115 · Other software · HumanSignal · reported by GitHubHigh 7.1
Label Studio is an a popular open source data labeling tool. Versions prior to 1.9.2 have a cross-site scripting (XSS) vulnerability that could be exploited when an authenticated user uploads a crafted image file for their avatar that gets rendered as a HTML file on the website. Executing arbitrary JavaScript could result in an attacker performing malicious actions on Label Studio users if they visit the crafted avatar image. For an example, an attacker can craft a JavaScript payload that adds a new Django Super Administrator user if a Django administrator visits the image. The file `users/functions.py` lines 18-49 show that the only verification check is that the file is an image by extracting the dimensions from the file. Label Studio serves avatar images using Django's built-in `serve` view, which is not secure for production use according to Django's documentation. The issue with the Django `serve` view is that it determines the `Content-Type` of the response by the file extension in the URL path. Therefore, an attacker can upload an image that contains malicious HTML code and name the file with a `.html` extension to be rendered as a HTML page. The only file extension validat
- Product
- label-studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddocs.djangoproject.comgithub.com
Jan 22, 2024Project files may contain malicious contents which the software will use to create files on the filesystem.CVE-2022-45792 · Other software · Omron · reported by ot-cert@dragos.comHigh 7.8
Project files may contain malicious contents which the software will use to create files on the filesystem. This allows directory traversal and overwriting files with the privileges of the logged-in user.
- Product
- Sysmac Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 17, 2024Studio Network Solutions ShareBrowser before 7.0 on macOS mishandles signature verification, aka PMP-2636.CVE-2023-44077 · Other software · Studionetworksolutions · reported by MITRECritical 9.8
Studio Network Solutions ShareBrowser before 7.0 on macOS mishandles signature verification, aka PMP-2636.
- Product
- Sharebrowser
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordkhronokernel.comsupport.studionetworksolutions.com
Jan 16, 2024Prior to v176, when opening a new project Meta Spark Studio would execute scripts defined inside of a package.json file included as part of that project.CVE-2024-23347 · Other software · Meta Platforms, Inc · reported by cve-assign@fb.comHigh 7.8
Prior to v176, when opening a new project Meta Spark Studio would execute scripts defined inside of a package.json file included as part of that project. Those scripts would have the ability to execute arbitrary code on the system as the application.
- Product
- Meta Spark Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordfacebook.comfacebook.com
Jan 10, 2024Sysmac Studio installs executables in a directory with poor permissions.CVE-2022-45793 · Other software · Omron · reported by ot-cert@dragos.comMedium 5.5
Sysmac Studio installs executables in a directory with poor permissions. This can allow a locally-authenticated attacker to overwrite files which will result in code execution with privileges of a different user.
- Product
- Sysmac Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Jan 9, 2024 A CWE-502: Deserialization of untrusted data vulnerability exists that could allow an attacker logged in with a user level account to gain higher privileges byCVE-2023-7032 · Other software · Schneider Electric · reported by cybersecurity@se.comHigh 7.8
A CWE-502: Deserialization of untrusted data vulnerability exists that could allow an attacker logged in with a user level account to gain higher privileges by providing a harmful serialized object.
- Product
- Easergy Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddownload.schneider-electric.comdownload.schneider-electric.com
Jan 9, 2024Visual Studio Elevation of Privilege VulnerabilityCVE-2024-20656 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.8
Visual Studio Elevation of Privilege Vulnerability
- Product
- Microsoft Visual Studio 2017 version 15.9 (includes 15.0 - 15.8)
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Jan 9, 2024NET, .NET Framework, and Visual Studio Security Feature Bypass VulnerabilityCVE-2024-0057 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comCritical 9.1
NET, .NET Framework, and Visual Studio Security Feature Bypass Vulnerability
- Product
- .NET 8.0
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Jan 8, 2024Dataiku DSS before 11.4.5 and 12.4.1 has Incorrect Access Control that could lead to a full authentication bypass.CVE-2023-51717 · Other software · Dataiku · reported by MITRECritical 9.8
Dataiku DSS before 11.4.5 and 12.4.1 has Incorrect Access Control that could lead to a full authentication bypass.
- Product
- Data Science Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recorddataiku.comdoc.dataiku.com
Jan 2, 2024A vulnerability, which was classified as problematic, was found in Acumos Design Studio up to 2.0.7.CVE-2018-25097 · Other software · Acumos · reported by VulDBLow 3.5
A vulnerability, which was classified as problematic, was found in Acumos Design Studio up to 2.0.7. Affected is an unknown function. The manipulation leads to cross site scripting. It is possible to launch the attack remotely. Upgrading to version 2.0.8 is able to address this issue. The name of the patch is 0df8a5e8722188744973168648e4c74c69ce67fd. It is recommended to upgrade the affected component. The identifier of this vulnerability is VDB-249420.
- Product
- Design Studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Dec 29, 2023Visual Studio Code Python Extension Remote Code Execution VulnerabilityCVE-2020-17163 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.8
Visual Studio Code Python Extension Remote Code Execution Vulnerability
- Product
- Python extension for Visual Studio Code
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Dec 15, 2023Path traversal vulnerability in AVEVA Edge (formerly InduSoft Web Studio) versions R2020 and prior allows an unauthenticated user to steal the Windows access toCVE-2021-42797 · Other software · Aveva · reported by MITREHigh 7.5
Path traversal vulnerability in AVEVA Edge (formerly InduSoft Web Studio) versions R2020 and prior allows an unauthenticated user to steal the Windows access token of the user account configured for accessing external DB resources.
- Product
- Edge
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Dec 15, 2023An issue was discovered in ExecuteCommand() in AVEVA Edge (formerly InduSoft Web Studio) versions R2020 and prior that allows unauthenticated arbitrary commandsCVE-2021-42796 · Other software · Aveva · reported by MITRECritical 9.8
An issue was discovered in ExecuteCommand() in AVEVA Edge (formerly InduSoft Web Studio) versions R2020 and prior that allows unauthenticated arbitrary commands to be executed.
- Product
- Edge
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Dec 15, 2023An issue was discovered in AVEVA Edge (formerly InduSoft Web Studio) versions R2020 and prior.CVE-2021-42794 · Other software · Aveva · reported by MITREMedium 5.3
An issue was discovered in AVEVA Edge (formerly InduSoft Web Studio) versions R2020 and prior. The application allows a client to provide a malicious connection string that could allow an adversary to port scan the LAN, depending on the hosts' responses.
- Product
- Edge
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Dec 7, 2023An issue in studio kent mini-app on Line v13.6.1 allows attackers to send crafted malicious notifications via leakage of the channel access token.CVE-2023-43305 · Other software · Linecorp · reported by MITREHigh 8.2
An issue in studio kent mini-app on Line v13.6.1 allows attackers to send crafted malicious notifications via leakage of the channel access token.
- Product
- Line
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Dec 4, 2023EzViz Studio v2.2.0 is vulnerable to DLL hijacking.CVE-2023-41613 · Other software · ezviz · reported by MITREHigh 7.8
EzViz Studio v2.2.0 is vulnerable to DLL hijacking.
- Product
- ezviz_studio
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordpacketstormsecurity.compacketstormsecurity.com
Nov 28, 2023An issue in GitKraken GitLens before v.14.0.0 allows an attacker to execute arbitrary code via a crafted file to the Visual Studio Codes workspace trust componeCVE-2023-46944 · Other software · Gitkraken · reported by MITREHigh 7.8
An issue in GitKraken GitLens before v.14.0.0 allows an attacker to execute arbitrary code via a crafted file to the Visual Studio Codes workspace trust component.
- Product
- Gitlens
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordgithub.comsonarsource.com
Nov 14, 2023.NET, .NET Framework, and Visual Studio Elevation of Privilege VulnerabilityCVE-2023-36049 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comHigh 7.6
.NET, .NET Framework, and Visual Studio Elevation of Privilege Vulnerability
- Product
- Microsoft Visual Studio 2022 version 17.2
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Nov 14, 2023Visual Studio Denial of Service VulnerabilityCVE-2023-36042 · Computers, phones & browsers · Microsoft · reported by secure@microsoft.comMedium 6.2
Visual Studio Denial of Service Vulnerability
- Product
- Microsoft Visual Studio 2022 version 17.6
- What to do
- Apply the vendor’s update. The NVD record links to the advisory.
Full record and what to do →NVD recordmsrc.microsoft.commsrc.microsoft.com
Where this comes from: the exploited list is CISA’s Known Exploited Vulnerabilities catalog. Everything else is the whole National Vulnerability Database, where each record is published by the team that found the bug (Wordfence, Patchstack, WPScan, the vendors themselves and others); we show who. Exploit odds are FIRST’s EPSS, updated daily. Titles and categories are ours, so check the linked record before acting on a detail. For a write-up of the big ones, see our advisories. Every vendor, and every WordPress plugin and theme with a recorded flaw, also has its own page. All of it is free to reuse as JSON, CSV or RSS.
Weekly security brief
The flaws that hit local websites, every Friday.
One short email: what got exploited this week, which WordPress plugins broke, and what to check. Unsubscribe in one click.
Tell us what you're building.
A website, your marketing, a security check, an app, or the thing you've been running out of a spreadsheet for three years. A few lines is plenty.
Not ready to talk yet? Run the free website check and see what Google sees.